
Fake CAPTCHA Scams Trick Users into Malware Downloads
A resurgence of an old social engineering tactic uses convincing fake CAPTCHA interfaces to lure users into downloading and executing malicious software.
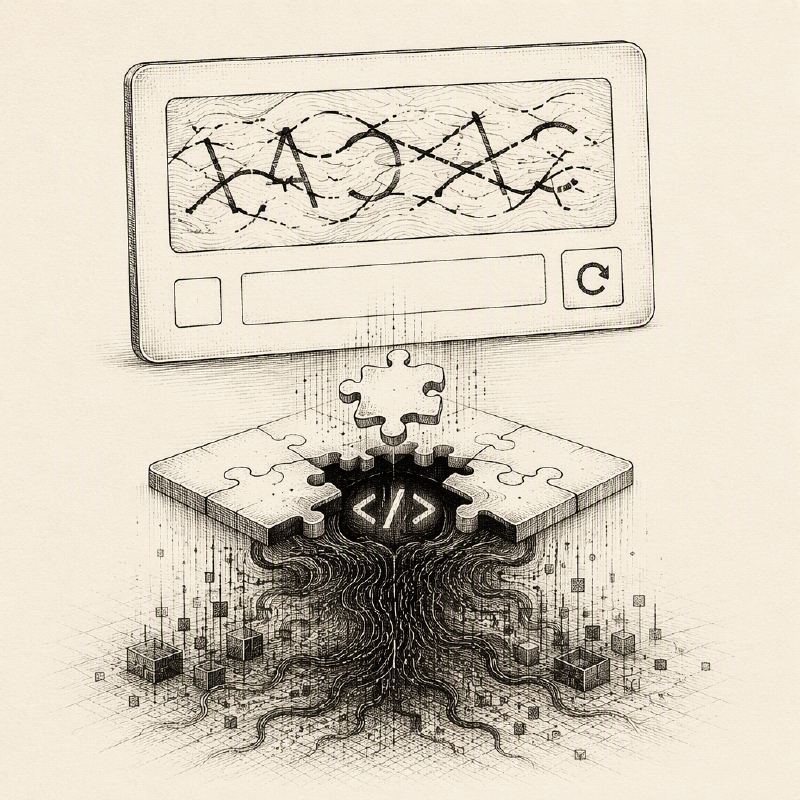
Cybercriminals are employing a sophisticated social engineering scheme that leverages the familiar process of CAPTCHA verification to trick unsuspecting users into compromising their own systems. This tactic, a modern iteration of older scams, relies on the user's ingrained trust in common web security measures to bypass their usual caution.
The core of the scam involves presenting a fake CAPTCHA challenge, often appearing on a seemingly legitimate website or as a pop-up. Users, accustomed to interacting with CAPTCHAs to prove they are not bots, proceed through the process without suspicion. However, instead of a simple verification, the "completion" of the CAPTCHA triggers the download of a malicious executable file.
Once downloaded, the malware may lie dormant or immediately begin its malicious activity. The exact payload can vary widely, ranging from information-stealing malware designed to harvest credentials and sensitive data, to ransomware that encrypts the victim's files, or even backdoors that grant attackers persistent access to the compromised system. The deceptive nature of the CAPTCHA interface is key to its effectiveness, as it masks the true intent of the download.
This method capitalizes on the psychological principle of familiarity and perceived security. CAPTCHAs are ubiquitous online, serving as a gatekeeper against automated abuse. By mimicking this trusted mechanism, attackers exploit users' reduced vigilance. The social engineering aspect is paramount; the scam doesn't rely on technical exploits of web browsers or operating systems, but rather on manipulating user behavior.
While the specific implementation details of these fake CAPTCHA pages can differ, the underlying principle remains the same: disguise malicious intent as a routine security procedure. Users are often directed to download an "installer," "plugin," or "update" that is, in reality, malware. The scam's success hinges on the user's failure to scrutinize the downloaded file or its source.
Security experts advise extreme caution when encountering unexpected download prompts, even if they appear to be part of a standard verification process. Users should always verify the legitimacy of the website and the downloaded file, and ensure their antivirus software is up-to-date and actively scanning. The resurgence of this scam highlights the persistent threat of social engineering and the need for continuous user education on cybersecurity best practices.
This evolving threat underscores the importance of a multi-layered security approach. Beyond technical defenses, fostering a security-aware mindset among users is crucial to mitigating the impact of such deceptive tactics. As attackers continually refine their methods, staying informed about emerging social engineering techniques is vital for both individuals and organizations.