
Discourse Image Pipeline Exploit Allows File Reads via JPEG Race Condition
A vulnerability in Discourse's image upload pipeline allowed basic users to read server files by chaining JPEG processing delays, Ghostscript, and ImageMagick.
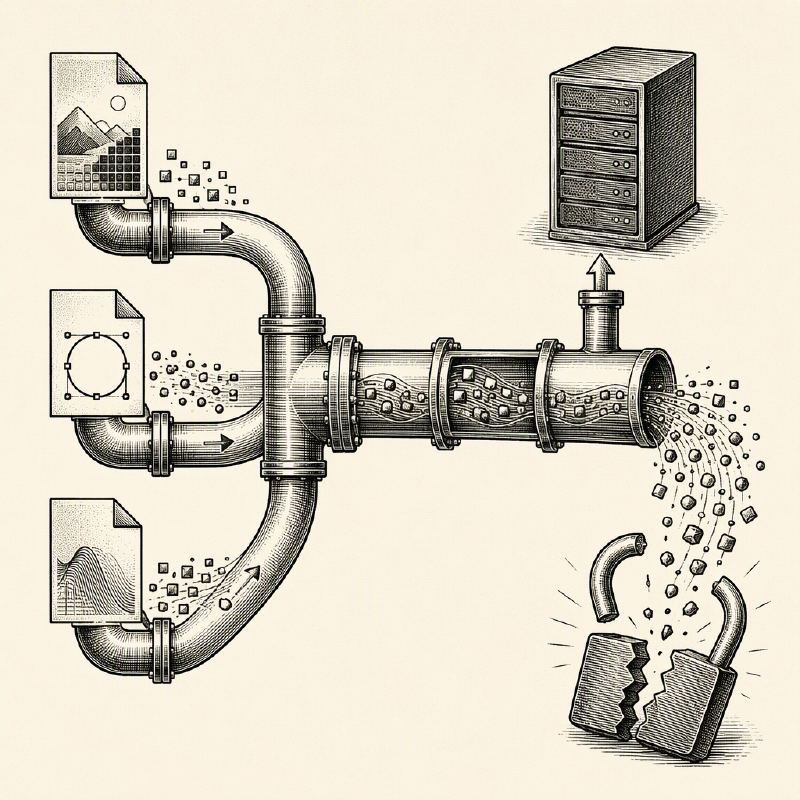
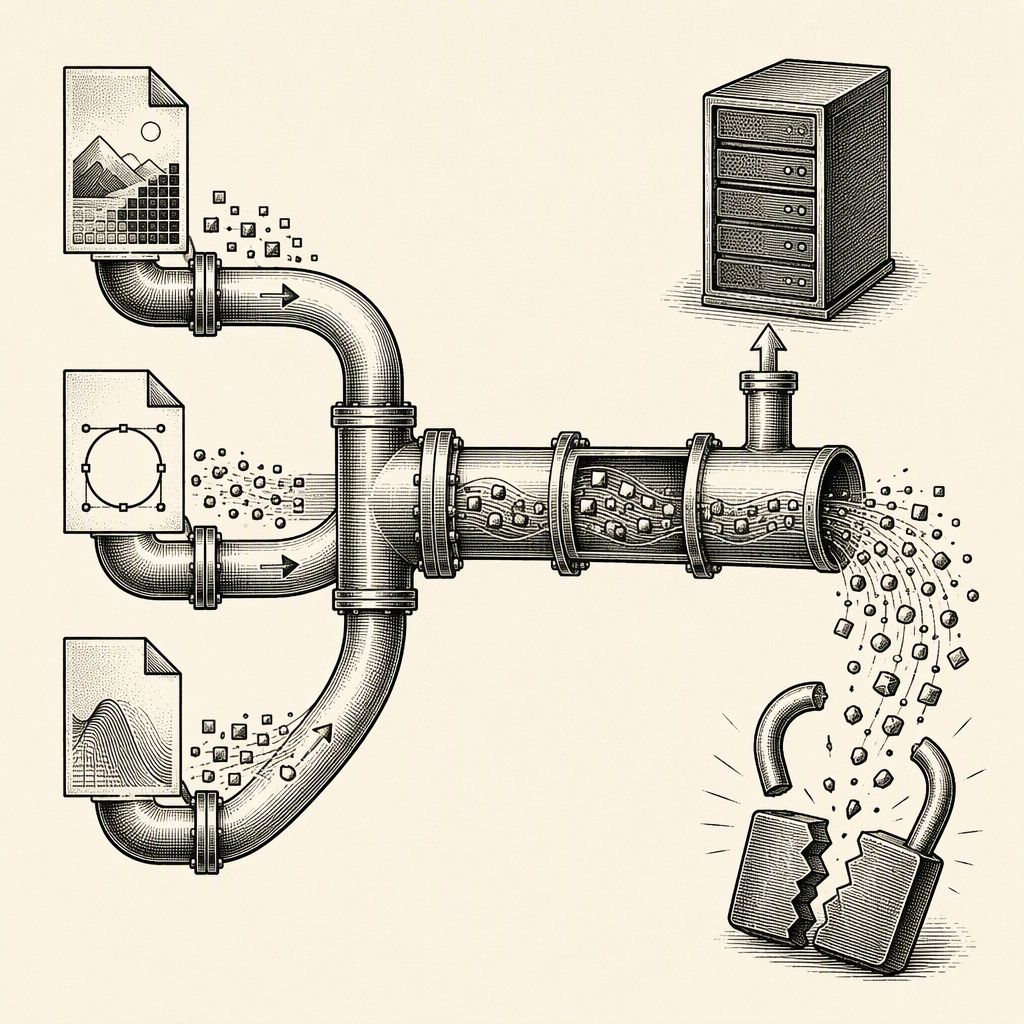
A critical vulnerability affecting the popular Discourse forum software allowed unauthenticated users to read sensitive server files by exploiting a complex chain of image processing flaws. The exploit, detailed by researchers from Searchlight Cyber, leveraged a time-of-check to time-of-use (TOCTOU) race condition within the image pipeline, combined with the capabilities of Ghostscript and ImageMagick.
Researchers discovered that while Discourse's default security policy blocked direct PostScript uploads, the image processing workflow still passed files to ImageMagick, which could then invoke Ghostscript. This created an opportunity to trick the system into processing malicious content disguised within seemingly legitimate image files. The attack required only a basic user account (Trust Level 0), making it accessible to even the lowest-tier members of a Discourse community.
The core of the file read exploit involved crafting a file that contained valid JPEG XL identification bytes but also embedded PostScript content. The initial upload handler, FastImage, would recognize the image dimensions, while the file's extension would direct ImageMagick to use Ghostscript for processing. Crucially, this was achieved without exploiting a direct vulnerability in Ghostscript itself or breaking its sandbox, instead relying on how the components interacted.
The TOCTOU vulnerability was exploited by uploading a file with a .msvg extension, which ImageMagick would process. After FastImage performed its initial checks, but before ImageMagick fully processed the image for its dominant color, the researchers would atomically replace the temporary file with a malicious SVG. This was made possible by using a specially crafted JPEG that deliberately slowed down the jpegoptim processing stage, creating a sufficient time window for the file replacement.
Once the malicious SVG was in place, ImageMagick's MSVG parser would interpret an embedded reference to Magick Scripting Language (MSL). This script could then be instructed to read a local server file and save its contents as an image. This image would then be incorporated into the upload storage flow, ultimately returning a normal download URL that contained the contents of the disclosed file.
In addition to the file read vulnerability, the research also uncovered a separate cache poisoning flaw. This issue allowed attackers to inject arbitrary JavaScript into the cache by manipulating unchecked color scheme cookies. This could lead to cross-site scripting (XSS) attacks, potentially executing JavaScript for anonymous visitors to the site.
Discourse has addressed both vulnerabilities. The image processing issue was mitigated by blocking specific delegates and restricting the image decoders that can be used. The cache poisoning flaw was fixed by implementing strict integer validation for cookie handling and ensuring these values are included in cache keys. Patched versions include Discourse 2026.6.0 and later releases, with specific advisories mentioning fixes in 2026.5.1, 2026.4.2, and 2026.1.5.
Administrators are strongly advised to update their Discourse instances to the latest versions to protect against these vulnerabilities. Relying solely on file extension restrictions is insufficient, as demonstrated by this exploit chain that bypassed such measures through clever manipulation of the image processing pipeline.