
Developer Hijacks Smart TV Ads Using Leaked eMudhra Keys
A Czech developer exploited leaked eMudhra intermediate CA private keys to block ads on his Samsung smart TV by redirecting ad traffic through a custom proxy.
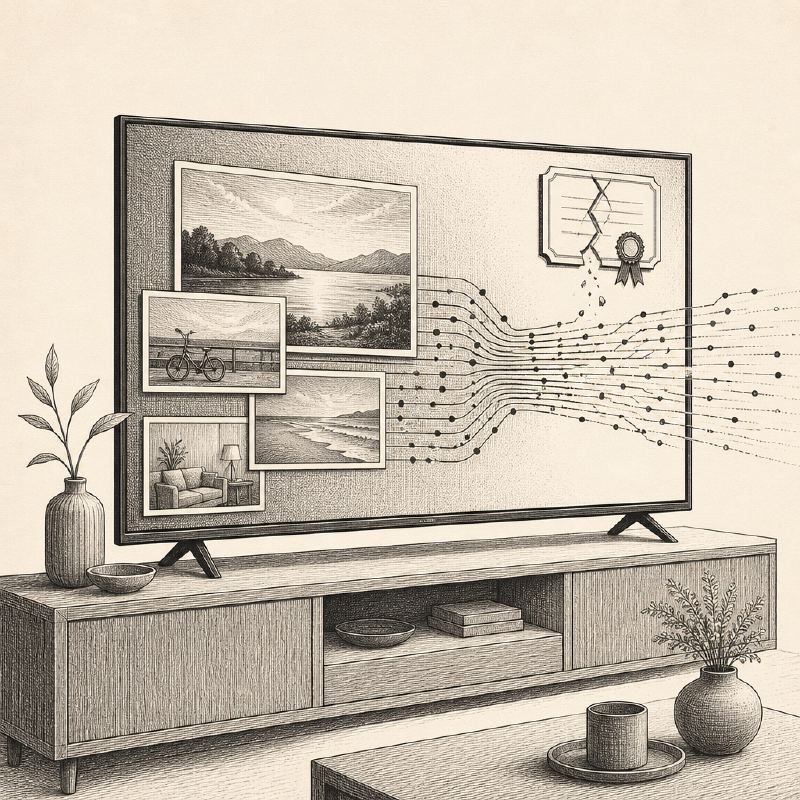
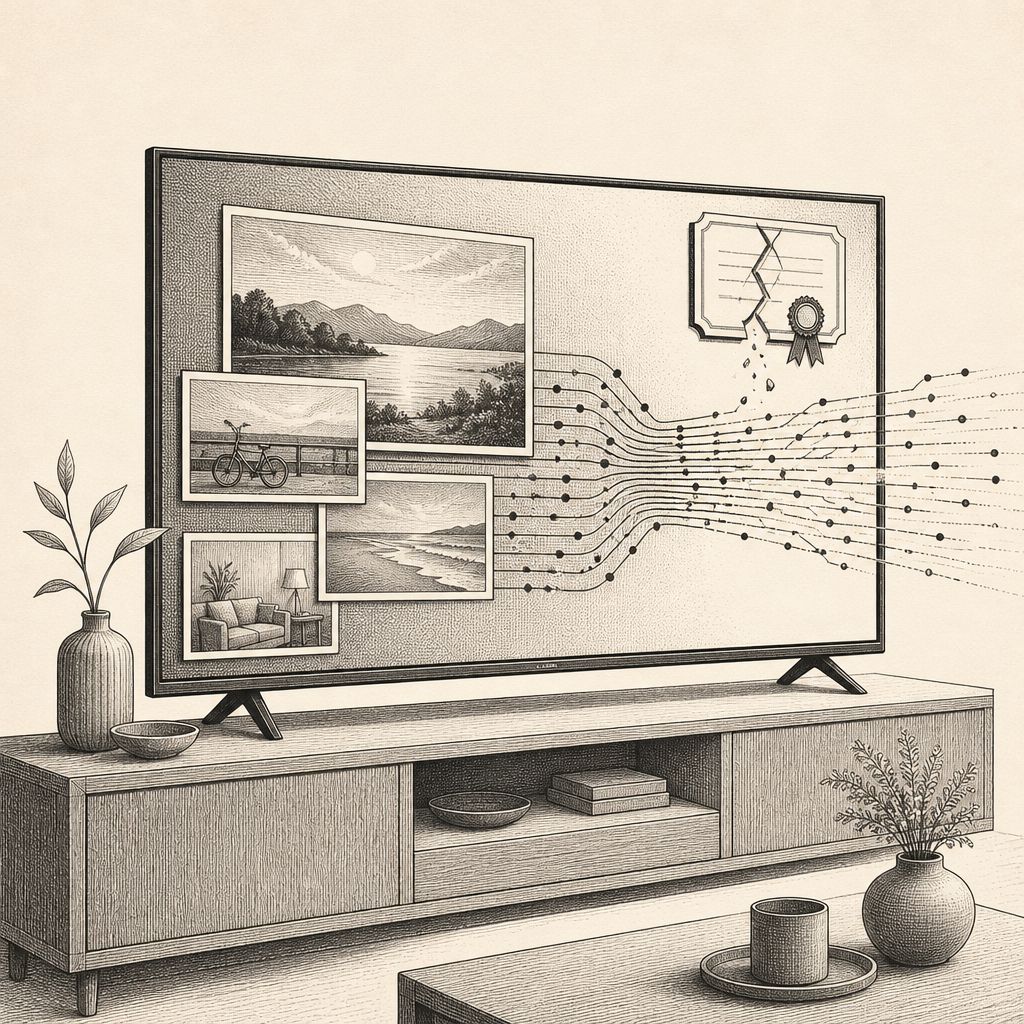
A security vulnerability stemming from the exposure of eMudhra's intermediate Certificate Authority (CA) private keys has inadvertently provided a novel method for blocking advertisements on smart televisions. Czech software developer Daniel Vrátil has detailed how he leveraged these compromised keys to intercept and modify traffic on his Samsung smart TV, effectively replacing unwanted ads with personal photographs.
Vrátil's project, published on GitHub, allows technically inclined users to replicate his success, provided their smart TV still trusts the compromised eMudhra certificates. The technique involves using mitmproxy, an open-source interactive HTTPS proxy, to inspect and manipulate the TV's network communications. By generating a forged eMudhra certificate for the TV's ad-serving domains and rerouting traffic to a local server, Vrátil was able to serve custom content.
The eMudhra certificate authority, based in India, reportedly issued over 60 million digital certificates. The compromise occurred when eight intermediate CA private keys were found to be inadequately protected, with some being easily guessable. eMudhra has since stated that certificate issuance was a minor part of its business and attributed the issue to a faulty script used for key generation.
This compromise means that attackers could forge eMudhra certificates to impersonate legitimate websites. However, Vrátil saw an opportunity for a more benign, albeit technically complex, application. His 2022 Samsung smart TV, which had not yet received an update to distrust the eMudhra certificates, allowed him to route all its traffic through mitmproxy.
He discovered that the TV's advertising mechanism involved relaying activity to an ad server, which then responded with ad content, often in JSON format. By creating a certificate for Samsung's advertising domains using one of the leaked eMudhra keys, and configuring his home router to direct requests for these domains to a server on his local network, Vrátil could serve his own content. His setup replaced ads with family photos hosted on his Network Attached Storage (NAS) device.
Furthermore, Vrátil's solution also discards tracking data sent to advertising domains, preventing it from reaching Samsung's servers. He noted that the process is not a simple one-click solution and requires users to analyze their own TV's traffic and adapt the code. The effectiveness of this method is contingent on devices continuing to trust the compromised eMudhra certificates, a situation that may change as vendors release updates.
Vrátil highlighted that while his personal use case is to block ads and tracking, the underlying vulnerability has broader implications. "The compromised eMudhra certificates open up a lot of opportunities for understanding and spoofing network requests from embedded devices, especially those that no longer receive security updates," he stated. This could enable more malicious activities, such as intercepting sensitive data or impersonating services.
He is currently exploring ways to prevent his TV from automatically updating its firmware, which could eventually revoke the trust in the eMudhra certificates and render his ad-blocking method obsolete. This pursuit itself presents a security trade-off, as disabling updates can leave the device vulnerable to other potential threats.