
Crypto Agility Becomes Essential as Certificate Lifespans Shrink
Enterprises face a new era of digital trust management, driven by shrinking certificate lifespans and the urgent need for automated cryptographic processes.
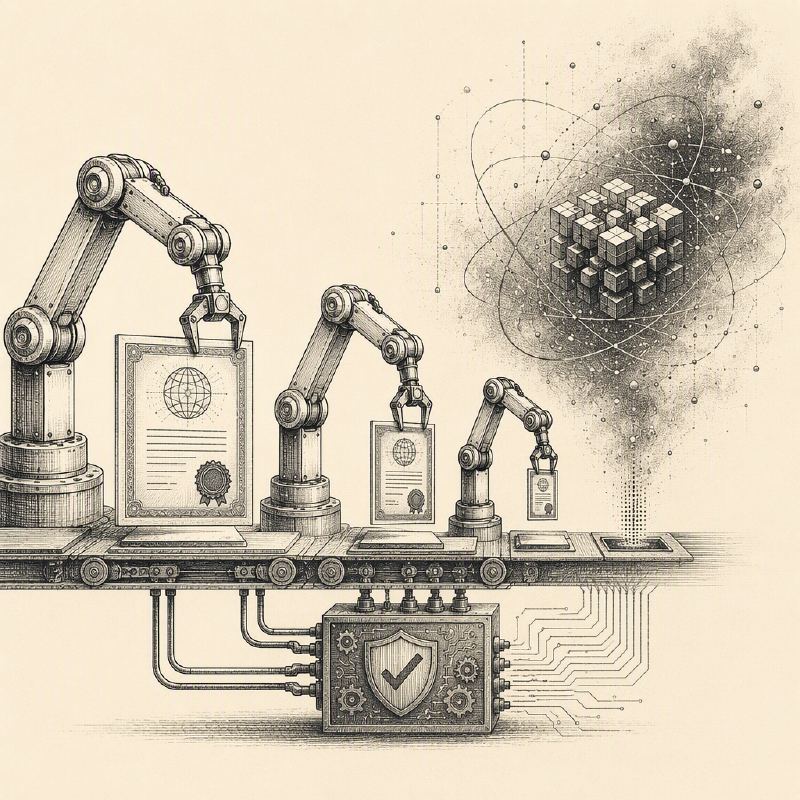
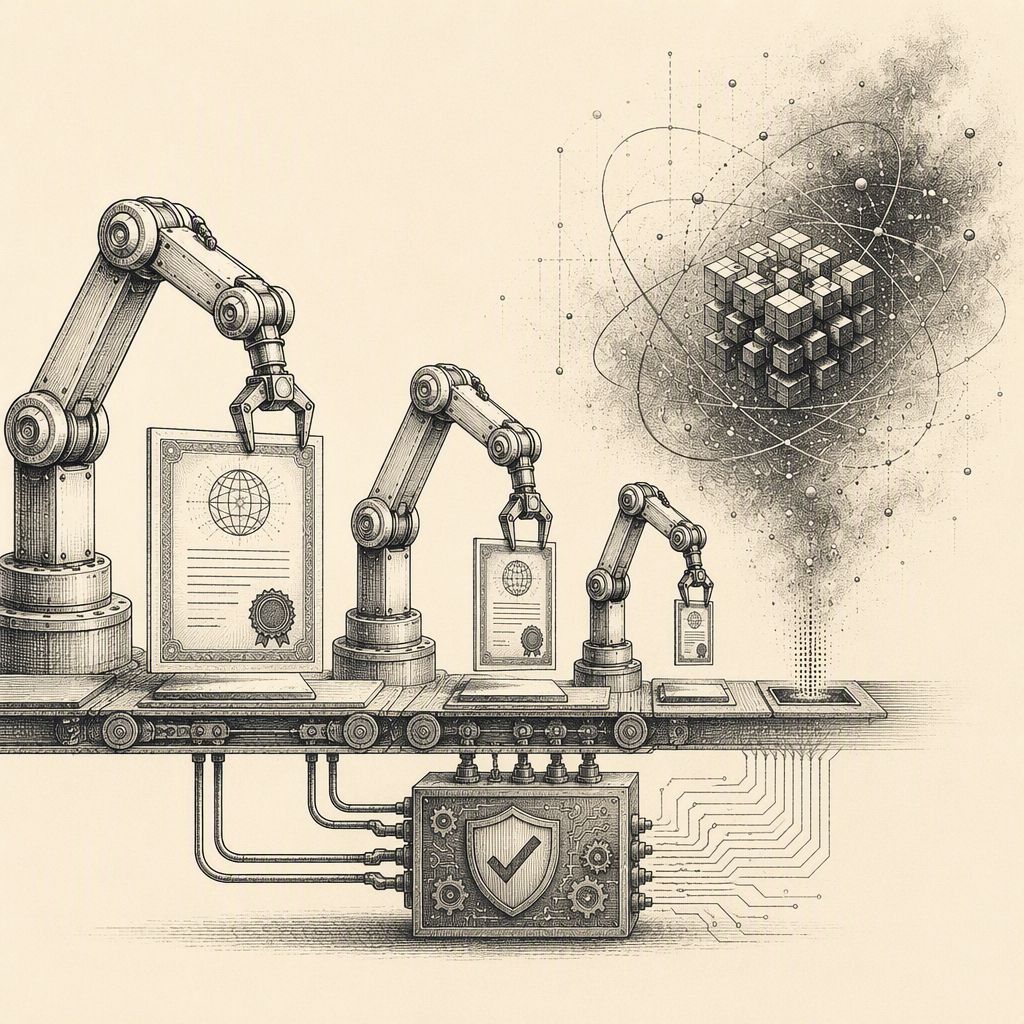
The landscape of enterprise security is undergoing a significant transformation, largely dictated by the accelerating pace of cryptographic evolution and the shrinking lifespans of digital certificates. This shift necessitates a proactive approach known as 'crypto agility,' enabling organizations to adapt quickly to new standards and threats. The traditional model of manual certificate renewal is rapidly becoming obsolete, replaced by automated protocols designed to manage the lifecycle of these critical trust anchors.
At the forefront of this automation is the Automated Certificate Management Environment (ACME) protocol. ACME allows for the programmatic issuance, renewal, and revocation of digital certificates, drastically reducing the administrative burden and the risk of human error associated with manual processes. As certificate validity periods continue to shorten, often to mere months or even weeks, the ability to automate these renewals becomes not just a convenience but a fundamental requirement for maintaining continuous security and operational integrity.
Beyond external-facing certificates, the adoption of Mutual TLS (mTLS) is becoming increasingly vital for securing internal service-to-service communications. By requiring both the client and server to present valid certificates, mTLS extends cryptographic identity beyond user authentication and into the fabric of the network. This layered security approach is crucial for protecting sensitive data and preventing lateral movement by attackers within an enterprise's internal infrastructure, especially as microservices architectures become more prevalent.
Furthermore, the looming deadline for the transition to Post-Quantum Cryptography (PQC) presents another significant challenge and opportunity for crypto agility. As quantum computing capabilities advance, current encryption algorithms will become vulnerable. Organizations must begin planning and implementing strategies to migrate to PQC-resistant algorithms to ensure the long-term confidentiality and integrity of their data. This transition requires not only technical expertise but also strategic foresight and investment.
Implementing crypto agility involves a multi-faceted strategy. It requires a deep understanding of an organization's cryptographic inventory, robust automation tools, and a culture that prioritizes adaptability. Leaders must assess their current cryptographic practices, identify potential weaknesses, and develop a roadmap for adopting new technologies and protocols.
The implications of failing to embrace crypto agility are substantial. Outdated certificates can lead to service disruptions, security breaches, and loss of customer trust. In an increasingly complex threat landscape, where new vulnerabilities and cryptographic standards emerge regularly, a static approach to security is no longer viable. Organizations that proactively build crypto agility into their security posture will be better equipped to navigate the evolving digital trust environment and maintain a strong defense against emerging threats.
Ultimately, digital trust is no longer a static state but a dynamic process that requires continuous management and adaptation. By embracing automated certificate management, mTLS, and preparing for the PQC transition, enterprises can build the resilience needed to ensure ongoing security and maintain confidence in their digital interactions.