
Critical UEFI Firmware Flaw Allows Pre-Boot Code Execution
A critical vulnerability in the open-source EDK II UEFI firmware's PXE driver enables remote attackers to execute code before the operating system loads.
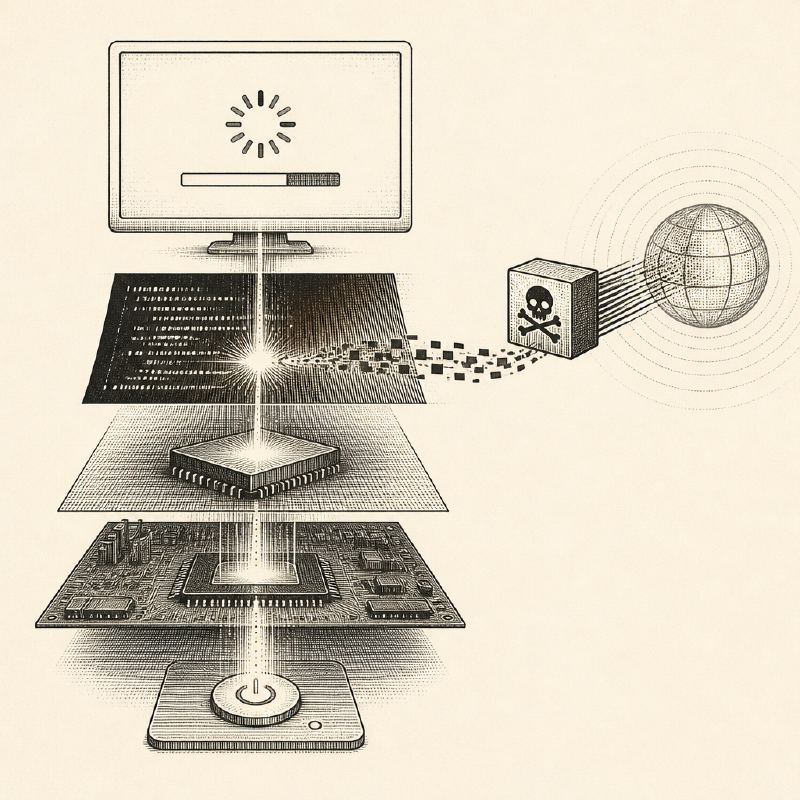
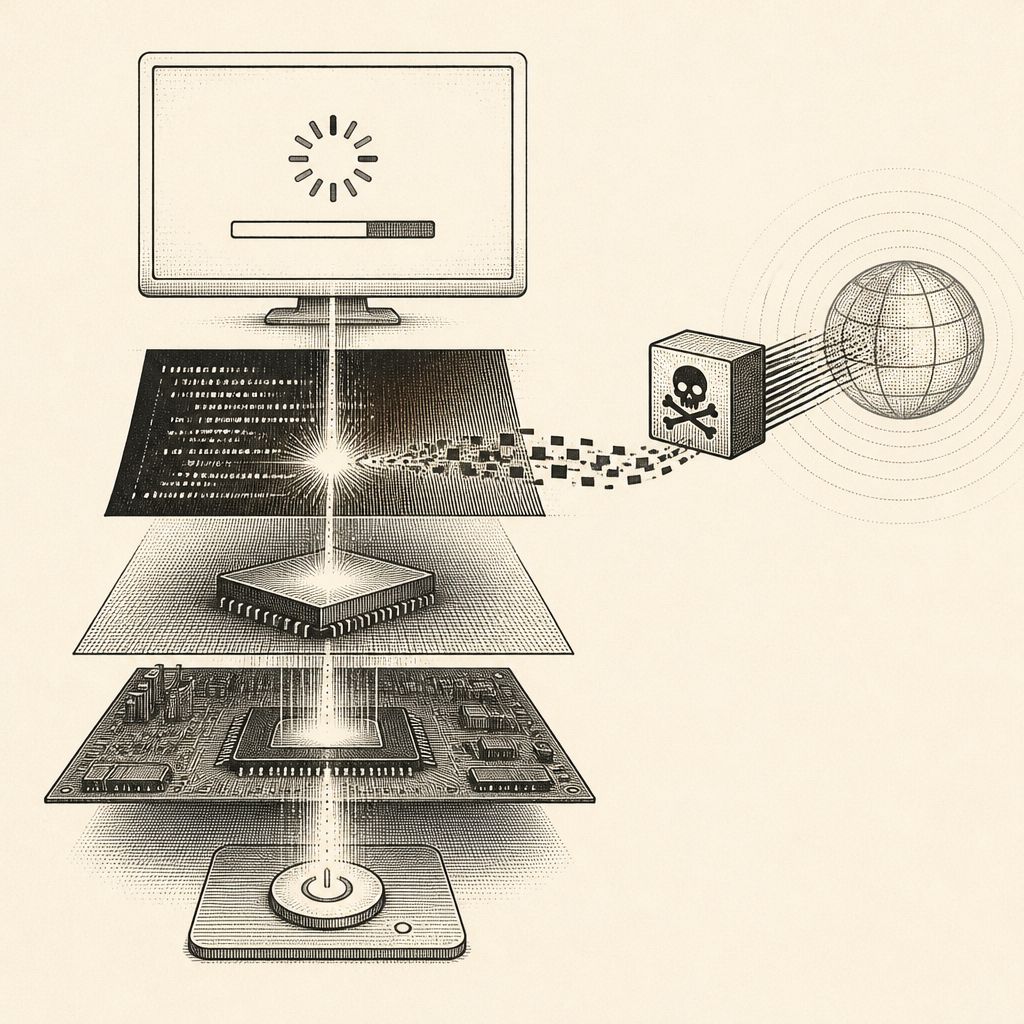
A critical vulnerability, tracked as CVE-2026-97631, has been discovered in the open-source EDK II firmware's PXE (Preboot Execution Environment) driver. This flaw, which has received a CVSS v4 score of 9.5, allows remote attackers to execute arbitrary code on a system before the operating system even begins to load. The vulnerability resides within the NetworkPkg package of EDK II, a foundational firmware project used by many hardware manufacturers to build UEFI firmware for servers, desktops, and laptops.
The exploit leverages oversized ICMP error messages sent during the PXE network boot process. The vulnerable UefiPxeBcDxe driver improperly handles these messages, copying data beyond the allocated buffer. This uncontrolled copying can lead to a system crash, disrupting critical operations like OS installations or recovery processes. More concerningly, a sophisticated attacker could craft a malicious ICMP message to inject and execute code at the highest privilege level, bypassing security measures like Secure Boot and measured boot.
This vulnerability poses a significant risk, particularly to data centers that heavily rely on PXE for automated server provisioning and rebuilding. The extended window of exposure during the PXE boot process, combined with the ability to execute code before OS-level defenses are active, provides attackers with a potent attack vector. The ease of exploitation, requiring only the ability to send a single ICMP error message to a booting client without any authentication or user interaction, amplifies the threat.
This discovery is part of a concerning trend of firmware-level security failures. Previous vulnerabilities, such as PKfail and LogoFAIL, have highlighted risks associated with firmware supply chains and image parsing. The PixieFail vulnerability, disclosed in January 2024, also targeted EDK II's network stack, demonstrating a recurring weakness in network boot operations within enterprise environments.
While a fix has been merged into the public EDK II code via pull request 13302, it is crucial to note that this does not mean immediate protection. Vendors must integrate this fix into their own firmware updates, a process that typically involves significant lead times. The advisory indicates "Not patched currently," underscoring the need for users to actively inquire with their hardware and firmware vendors about patch availability.
The fix involves implementing proper boundary checks and correcting pointer arithmetic to prevent buffer overflows. Oversized ICMP messages are now truncated, and the buffer is cleared before each copy operation to prevent residual data from previous messages from causing issues. Unit tests have been added to ensure the integrity of the fix.
This vulnerability was discovered by Alex Matrosov of Anthropic and Dan Holmes-Mitra of Google. The disclosure process faced a minor hiccup when the pull request was accidentally made public before the intended coordinated disclosure embargo, prompting a request from a maintainer for more private reporting of future issues.
To mitigate the risks until patches are widely available, organizations should restrict PXE boot traffic to isolated provisioning networks, block unexpected ICMP error messages directed at booting systems, and disable PXE on systems where it is not required. Reviewing CISA and NSA guidance on Secure Boot hardening is also recommended.