
Cloudflare Launches Post-Quantum Geo-Restricted Key Manager to Enhance Data Sovereignty
Cloudflare introduces a beta version of its Post-Quantum GeoKey Manager, integrating advanced cryptography to ensure data decryption keys remain within customer-defined geographical boundaries.
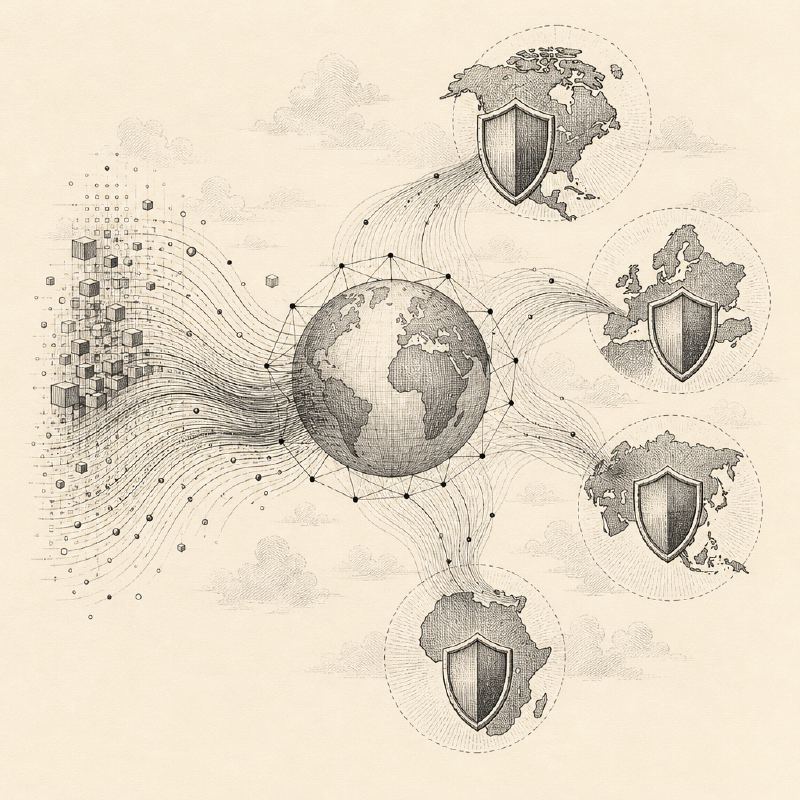
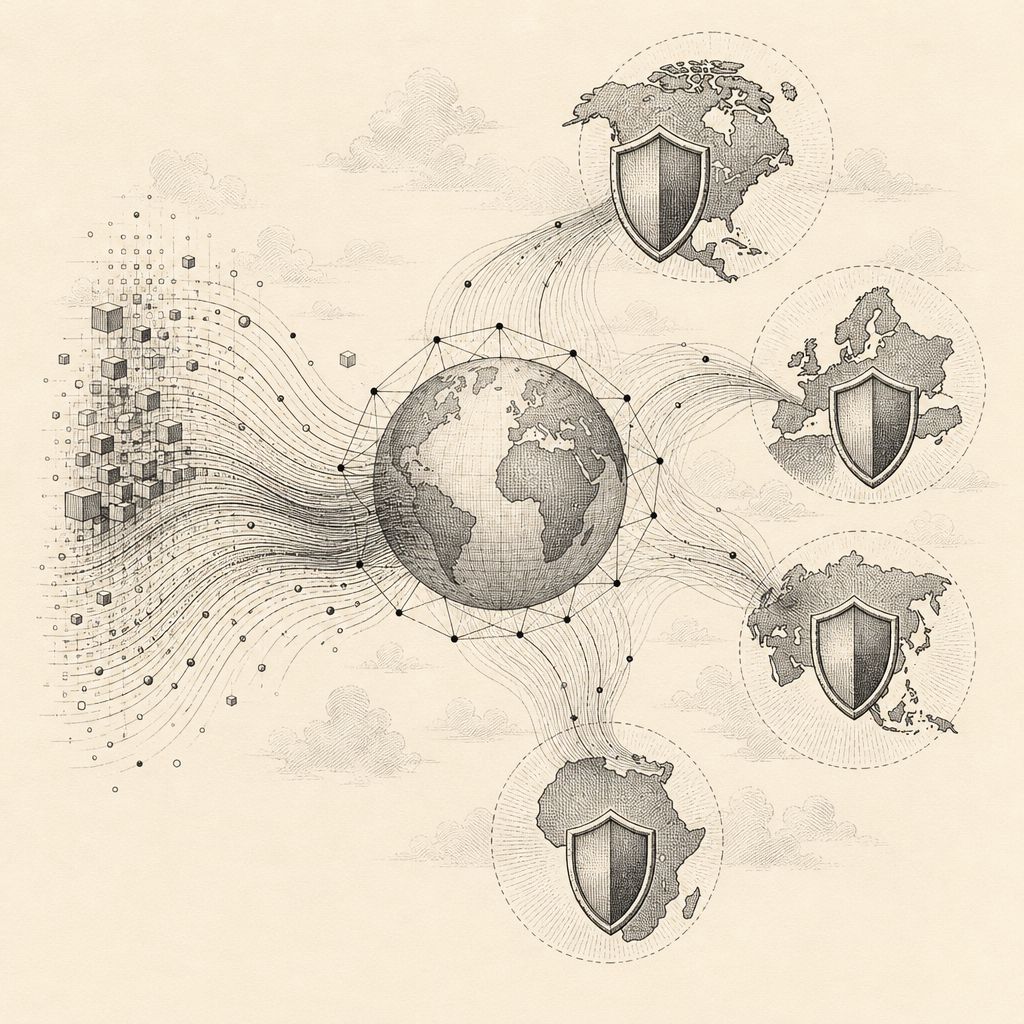
Cloudflare has announced the beta launch of its Post-Quantum GeoKey Manager, a significant enhancement to its Data Localization Suite. This new system is designed to ensure that decryption keys for customer data are exclusively accessible within specified geographical regions, directly addressing the growing threat of 'harvest now, decrypt later' attacks and bolstering data sovereignty.
The GeoKey Manager operates by wrapping decryption keys in a manner that permits decryption only by Cloudflare servers located within the customer's approved geography. This granular control is crucial for organizations, particularly in sectors like government, finance, and healthcare, which handle highly sensitive data that must remain protected for extended periods. The 'harvest now, decrypt later' strategy, where adversaries stockpile encrypted data with the intent to decrypt it once quantum computers become powerful enough, is a primary concern that this new manager aims to mitigate.
This initiative is also a key step in Cloudflare's broader strategy to migrate all its products to post-quantum (PQ) cryptography. While general availability is slated for Q1 2027, the beta launch marks a critical milestone in preparing for a future where current public-key encryption methods may no longer be secure against quantum adversaries.
The evolution of GeoKey Manager traces back to 2017 with the introduction of geo-restricted transport layer security (TLS) keys, which allowed customers to control the specific Cloudflare network locations where their private TLS keys could be unwrapped. This was further refined in 2022 with ciphertext policy attribute-based encryption (ABE), enabling geographic requirements to be expressed using attributes like country or region, offering greater flexibility.
For its post-quantum transition, Cloudflare has adopted a hybrid approach utilizing ML-KEM-768, a NIST standard, and X25519. This system employs two types of keys: a symmetric regional root key tied to a specific geographic area, and an application-specific key pair derived from it for individual services. This design ensures that private key material is protected against future quantum decryption threats while strictly enforcing regional boundaries for key usage.
In its current iteration, the GeoKey Manager serves as the foundational element for Cloudflare's data sovereignty solutions, dictating where protected decryption keys can be utilized. The system ensures high availability and performance by logically separating its global network while maintaining security. If a request is routed to a region that lacks the necessary regional root key for decryption, the request will fail closed, preventing any potential out-of-region key unwrapping and guaranteeing that regional root keys remain confined to their designated areas.
Customers will select their preferred region, and Cloudflare will manage the underlying infrastructure required to unwrap their private keys within that boundary. This new manager is designed to provide robust protection against advanced threats while supporting the complex regulatory and data sovereignty requirements faced by global organizations.