
Cloudflare Application Profiles Enhance Web Security with Positive Security Model
Cloudflare introduces Application Profiles, a new feature that enforces positive security by learning and allowing only expected HTTP request structures, significantly reducing the attack surface.
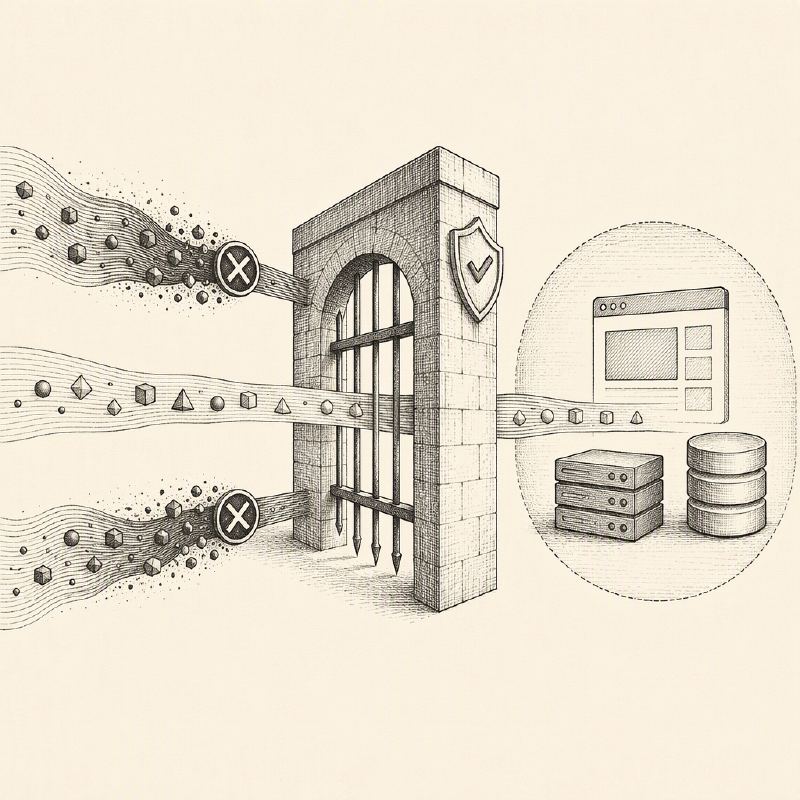
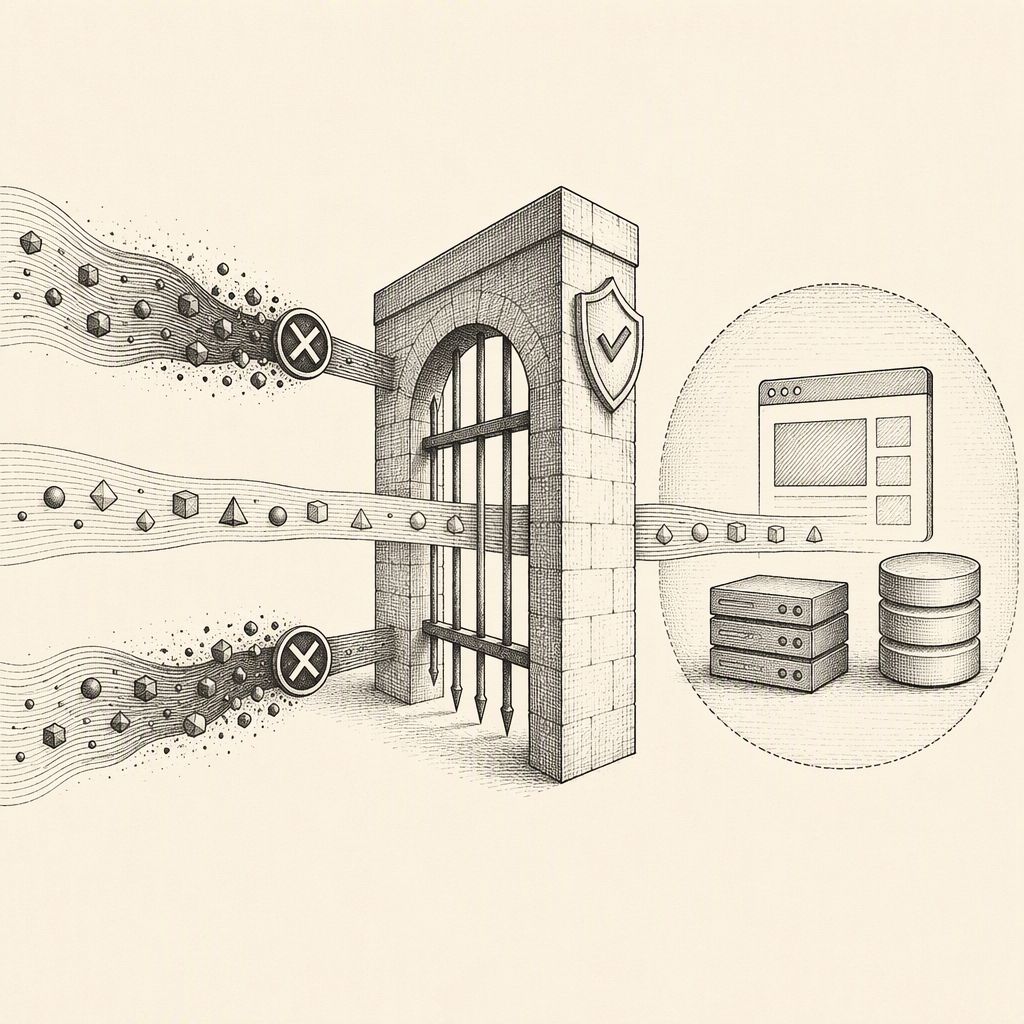
Cloudflare has launched Application Profiles, a new security feature designed to enforce a positive security policy for web applications. This innovative approach moves beyond traditional signature-based Web Application Firewall (WAF) rules by analyzing the structure and format of HTTP requests to identify deviations from learned 'good' traffic patterns. By allowing only conforming requests, Cloudflare aims to significantly reduce the attack surface area, offering a more robust defense against evolving threats, particularly those amplified by AI.
The increasing sophistication of AI models, including large language models (LLMs), has lowered the barrier to entry for launching complex attacks. Attackers can now use AI to generate malicious payloads, probe applications autonomously, and mutate their tactics based on application feedback. While existing tools like managed WAF rules and machine learning detections remain crucial for identifying known attack techniques such as SQL injection and cross-site scripting, the sheer volume and novelty of AI-generated threats necessitate a more proactive defense strategy. Application Profiles offer this by learning what legitimate requests look like, rather than solely focusing on identifying known malicious patterns.
The core of Application Profiles lies in its ability to learn the expected structure and format of HTTP requests from observed traffic. Once a profile is established, an always-on validation layer is deployed to live traffic. This layer evaluates each request against the learned profile, flagging any non-conformities. These deviations can range from unexpected characters in a search field to malformed universally unique identifiers (UUIDs) or values outside an expected numeric range. Unlike traditional WAF rules, failing validation does not require a request to match a known attack signature; it simply needs to differ from the learned 'normal' behavior.
Once Cloudflare has learned the request structure, it can infer the purpose of each operation and understand the application's overall functionality. This deeper insight allows for the identification and prioritization of the most critical and vulnerable operations and fields within an application. This capability is particularly valuable for hardening applications against a wide array of attack vectors, including SQL injection, cross-site scripting, and remote code execution, by drastically narrowing the range of acceptable inputs.
Cloudflare is extending this positive security model, previously available for APIs through Schema Learning and Schema Validation, to web applications with Application Schema Profiles. Customers onboard an application, Cloudflare learns its profile, and then deploys continuous detection. The validation layer adds metadata to requests, indicating conformity or non-conformity. Customers can then analyze this data in Security Analytics and create Security Rules to enforce blocking of non-conforming requests. Initially, the feature is recommended to be used in observation mode to allow customers to review the impact of a profile before enabling enforcement, as non-conforming traffic is not always malicious and can result from legitimate application updates or new client behaviors.
The learning process for Schema Profiles analyzes various components of HTTP requests, including path variables, query parameters, headers, cookies, and the body structure (JSON or form-encoded). For each field, the system learns its data type (e.g., integer, string, boolean, UUID, enum) and specific constraints like numeric ranges, string lengths, and character classes. Customers can select specific operations for profiling, which Cloudflare identifies by HTTP method, hostname pattern, and path pattern. These operations can be automatically discovered or manually added, with profiling being triggered upon creation for manual entries or requiring explicit selection for discovered operations.
Application Profiles are currently in a closed beta for invited Enterprise customers who do not have API Security. Customers who already utilize Cloudflare's API Security features have immediate access. This rollout signifies Cloudflare's commitment to providing advanced, adaptive security solutions that can keep pace with the rapidly evolving threat landscape, especially in the age of AI-driven attacks.