
Cloud Penetration Testing Methodology Focuses on Trust Boundaries
Securelist details a structured approach to cloud penetration testing, emphasizing the critical trust boundaries between external, overlay, and underlay environments.
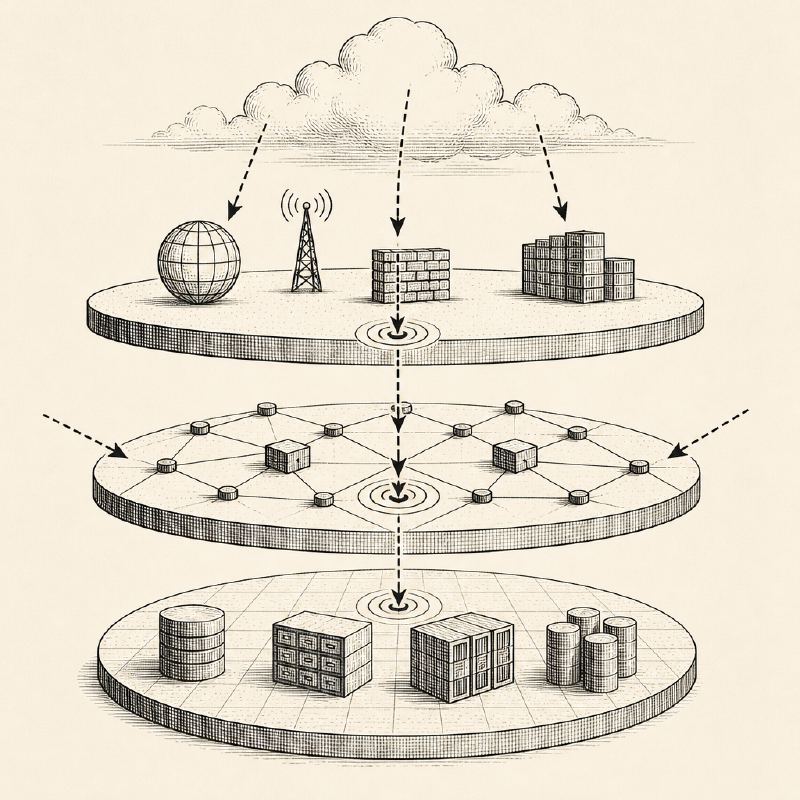
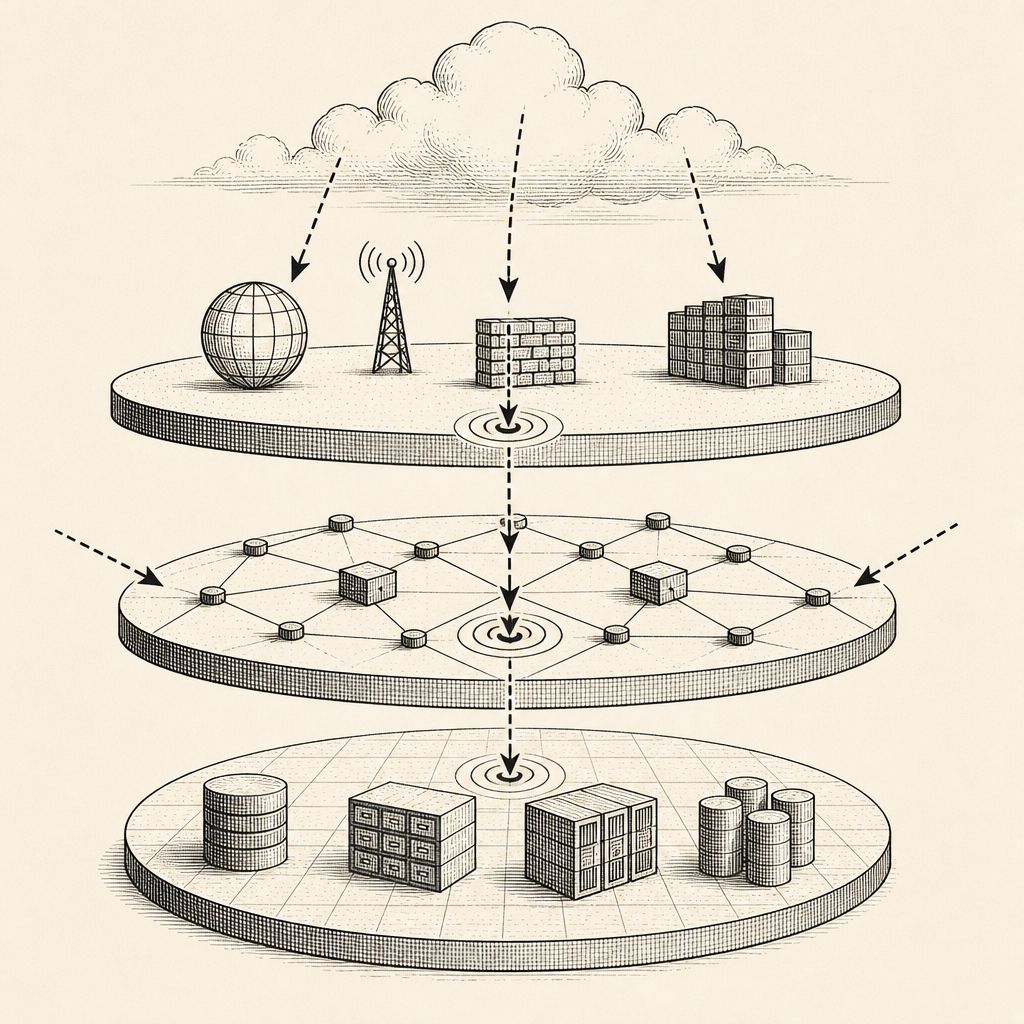
Penetration testing in cloud environments presents unique challenges compared to traditional web application security assessments. Securelist, in a recent article, outlines a methodology designed to systematically probe the security of cloud infrastructure by focusing on the "trust boundaries" between different operational zones. This approach moves beyond simply finding individual vulnerabilities to assessing whether an attacker can breach the logical separation between a cloud provider's services and its customers' data.
The methodology conceptualizes cloud environments using a three-zone model: External, Overlay, and Underlay. The External zone represents the customer-facing interfaces like management consoles and APIs. The Overlay zone, or tenant plane, encompasses the services and data managed directly by a tenant, such as virtual machines and databases. Finally, the Underlay zone is the provider's underlying infrastructure, analogous to a hotel's staff area, which is hidden from direct customer access. The core principle is that a secure cloud environment maintains strong trust boundaries, preventing unauthorized access or compromise across these zones.
Traditional cloud pentests often concentrate heavily on the External layer, which is important but only scratches the surface of potential attack vectors. Securelist's approach aims to uncover less obvious weaknesses by posing critical questions about an attacker's potential capabilities. These questions include whether an attacker can access data belonging to other tenants, compromise the cloud provider's own Identity and Access Management (IAM) service accounts, spread from a compromised runtime environment to other resources, affect provider-level infrastructure from low-trust segments, or achieve a virtual environment escape.
The article defines key terms crucial for understanding cloud security and pentesting. A "tenant" is a logically isolated unit within a cloud platform, while the "tenant plane" refers to the services and data a tenant directly manages. The "management console" is the primary customer interface at the External layer. "Service runtime" is where a provider's cloud product actually executes, such as in containers or virtual machines, managed by the "service management plane." Special attention is given to "IAM service accounts," which are digital identities for programs and services, and "context," which encompasses the attributes and credentials defining a subject's permissions and environment.
Understanding the "provider overlay" is central to this methodology. This is the provider's internal environment, inaccessible to customers under normal circumstances, but potentially reachable from a compromised "initial zone" within a tenant's environment. This internal layer includes network segments, internal APIs, and management components. The pentest aims to determine if an attacker can pivot from a tenant's isolated resources into this provider-controlled space.
The value of this pentesting methodology lies not just in identifying vulnerabilities, but in validating the effectiveness of security controls. Even a "negative result"—where a pentester fails to breach a specific boundary—is considered a valuable finding. It confirms that certain protections are working in practice, though it doesn't guarantee the impossibility of other attack paths. This structured approach helps organizations and providers better understand their actual security posture beyond theoretical configurations.
By dissecting cloud security into these distinct zones and focusing on the integrity of trust boundaries, this methodology provides a more comprehensive framework for assessing the security of complex cloud deployments. It encourages testers to think holistically about potential lateral movement and privilege escalation scenarios that could have far-reaching consequences, moving beyond isolated vulnerability discovery.