
Cisco Secure Email Gateway Under Active Attack for Critical File Write Vulnerability
Cisco is warning of active exploitation of a critical vulnerability in its Secure Email Gateway, allowing unauthenticated attackers to write arbitrary files and execute commands as root.
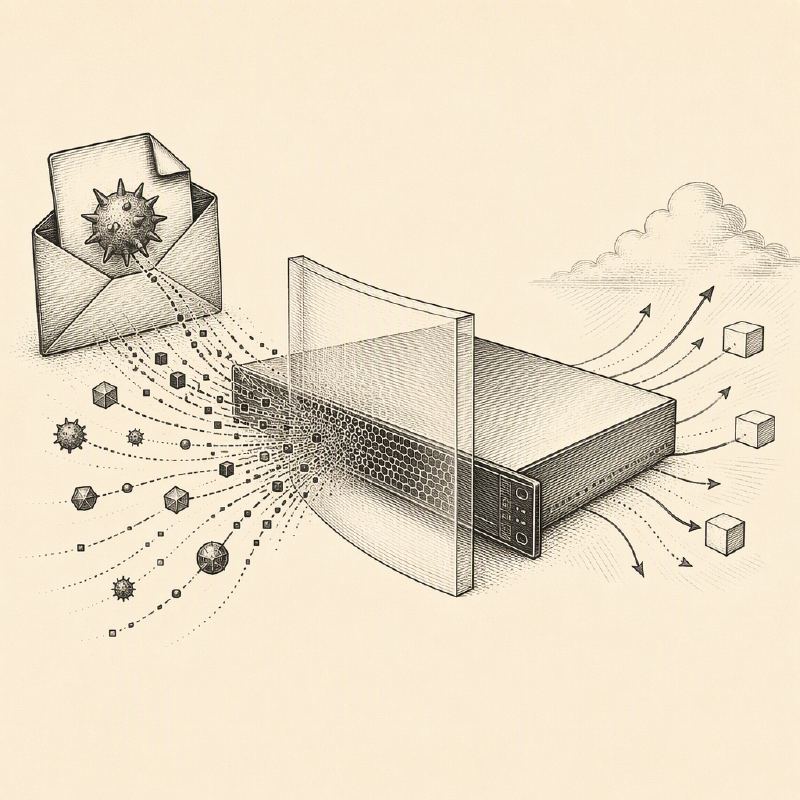
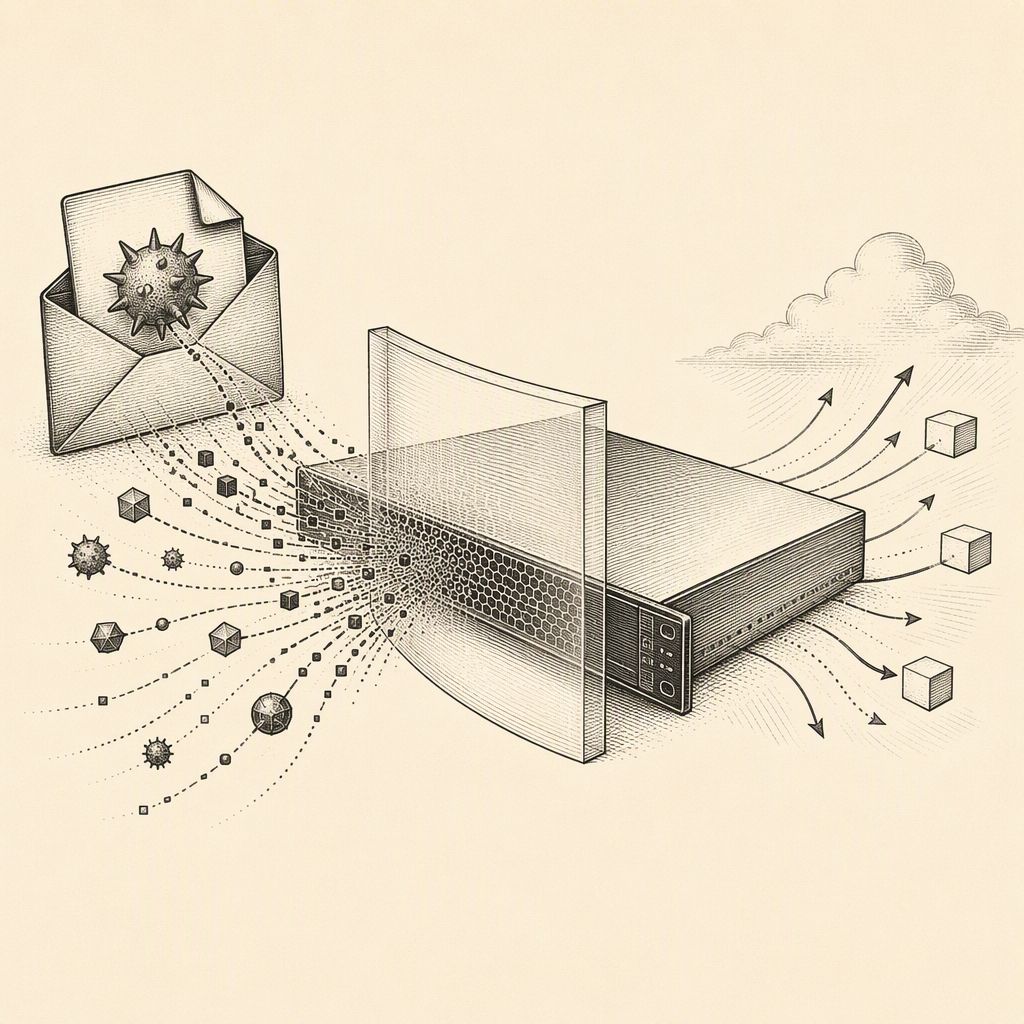
Cisco has issued a stern warning regarding a critical vulnerability affecting its Secure Email Gateway (SEG) products, which is currently being actively exploited in the wild. The flaw, identified as CVE-2026-XXXX (specific CVE not yet publicly disclosed by Cisco in this advisory), allows unauthenticated attackers to write arbitrary files to the appliance's operating system.
Exploitation of this vulnerability is initiated through a specially crafted email attachment. When such an email is processed by the vulnerable SEG appliance, an attacker can leverage the flaw to gain the ability to write files to the underlying operating system. This capability is particularly dangerous as it can pave the way for further malicious actions.
The ultimate impact of a successful exploitation is the ability for an attacker to execute arbitrary commands on the affected gateway with root privileges. This level of access would allow an adversary to fully compromise the email filtering appliance, potentially disrupting email security, exfiltrating sensitive data, or using the gateway as a pivot point into the organization's internal network.
Cisco's advisory emphasizes the critical nature of this vulnerability and urges customers to apply available patches immediately. The company has released security updates to address the issue and recommends that users consult their specific product documentation for the patching process. Given the active exploitation, prompt remediation is paramount to prevent further compromise.
While the exact scope of affected versions and the full technical details of the exploit are still emerging, the advisory highlights the risk to organizations relying on Cisco's Secure Email Gateway for their email security infrastructure. The ability for an unauthenticated attacker to gain root access on such a critical security appliance represents a significant threat.
This incident underscores the ongoing challenges in securing email gateways, which are often prime targets for attackers seeking to infiltrate networks or disrupt communications. The vulnerability's nature, allowing arbitrary file writes and command execution, is a common pattern seen in critical exploits targeting network appliances.
Organizations using Cisco Secure Email Gateway should prioritize reviewing Cisco's official advisories and implementing the necessary security updates. Monitoring network traffic for any signs of suspicious activity related to email attachments or unusual command execution on the gateway should also be a key part of their incident response strategy.