
CISA Warns Critical Infrastructure Operators on Third-Party ICS Integrator Risks
CISA and the FBI have issued guidance highlighting significant cybersecurity risks for critical infrastructure operators when engaging third-party industrial control system (ICS) integrators.
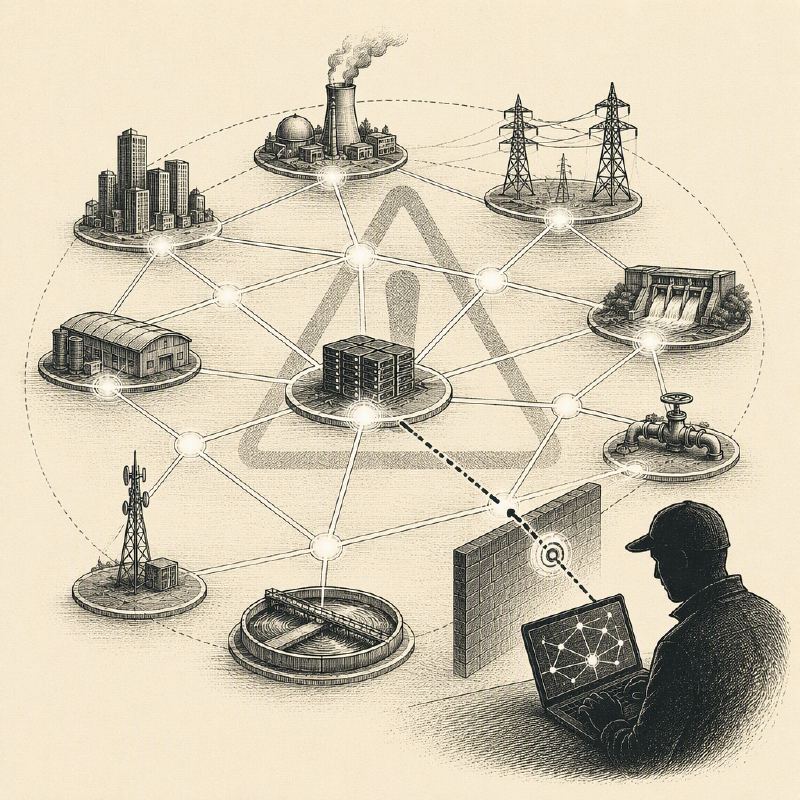
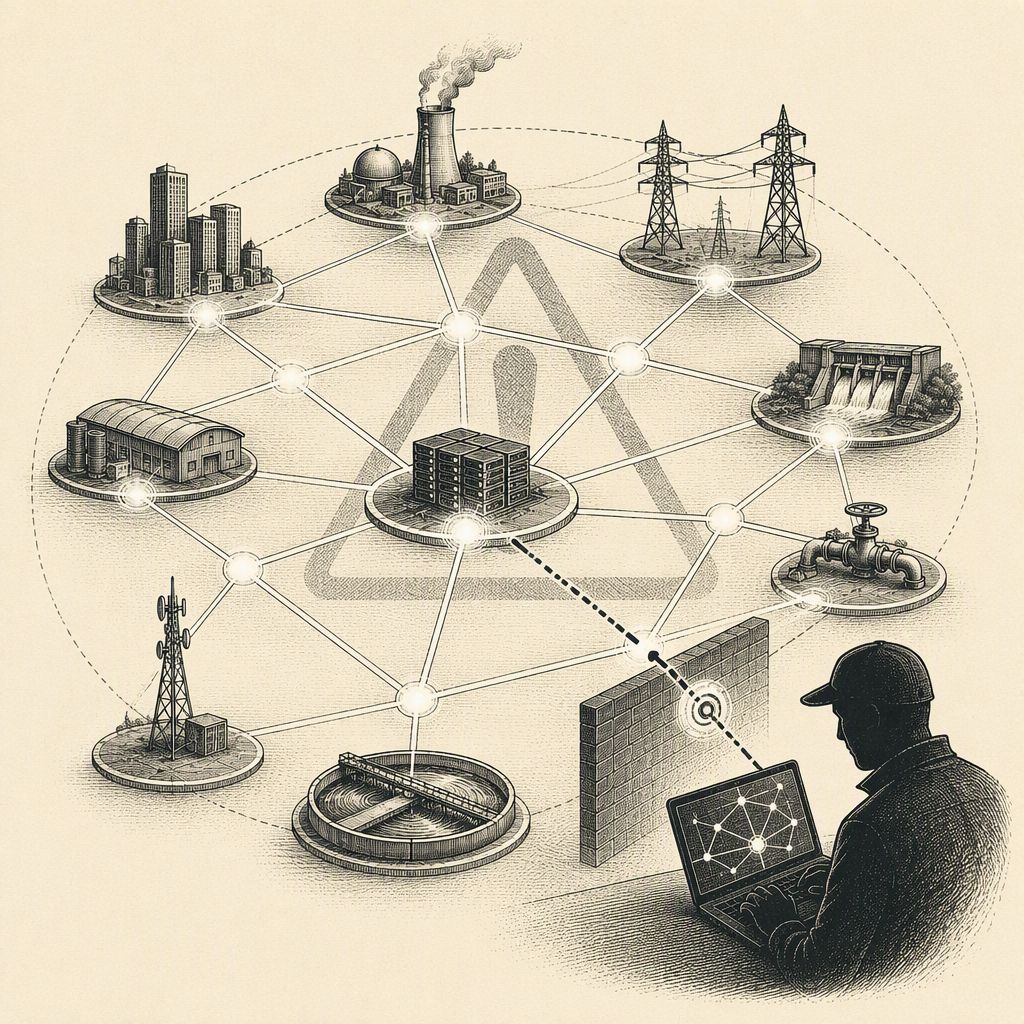
The U.S. Cybersecurity and Infrastructure Security Agency (CISA) and the Federal Bureau of Investigation (FBI) are alerting critical infrastructure operators to the inherent risks associated with employing third-party industrial control system (ICS) integrators. These integrators, crucial for services like control system design, installation, and operational data analysis, can inadvertently introduce vulnerabilities if not managed with stringent security protocols. The agencies emphasize that granting these third parties extensive access or control over industrial processes necessitates a strict adherence to the principle of least privilege (PoLP), ensuring they only have the minimum necessary access to perform their duties.
Failure to implement PoLP can create pathways for malicious actors to compromise critical infrastructure, potentially leading to disruptive and destructive effects on essential equipment and functions. The advisory stems from a recent incident where foreign cyber actors infiltrated the network of a U.S. industrial automation solutions company. This company provided services, including SCADA programming, to critical sectors such as power utilities and transportation.
Between March and April 2025, the threat actors navigated the compromised network, searching for terms like "customers" and "SCADA." They subsequently compiled approximately 800 files into nine .zip archives, believed to be for exfiltration. This stolen data, including customer SCADA information, ICS device details, and schematics, could be leveraged by adversaries to plan and execute future disruptive attacks against operational environments, threatening the continuity of critical services.
CISA and the FBI urge critical infrastructure operators to conduct thorough risk assessments before onboarding third-party integrators. These assessments should scrutinize contracts involving access to industrial systems, evaluating potential impacts on data autonomy and process controls. Key considerations include the hardware and software supply chain vulnerabilities introduced by integrator equipment, as well as the overall IT and OT security posture of the integrator's devices and networks.
When evaluating foreign-owned integrators, operators must also incorporate geopolitical considerations into their risk assessments. This includes understanding how the entity might be targeted directly or indirectly due to the current geopolitical climate. Specific questions operators should ask include what organizational data the integrator will store or access, where this data will be physically located (especially if international storage is involved, subjecting data to foreign laws), and the security implications of any remote access the integrator requires for operational support.
The potential for malicious actors to pivot from an integrator's compromised network into the critical infrastructure's operational environment is a significant concern. Therefore, operators must carefully assess the security of their remote connections and ensure they can maintain independent operations even if third-party access is disrupted or compromised. This proactive approach is vital for safeguarding the resilience and security of the nation's essential services against evolving cyber threats.