
Brevo Supply Chain Attack Delivers WordPress Backdoors and ClickFix Malware
A supply chain attack on Brevo injected malicious JavaScript into its services, compromising over 100,000 WordPress sites with backdoors and malware prompts.
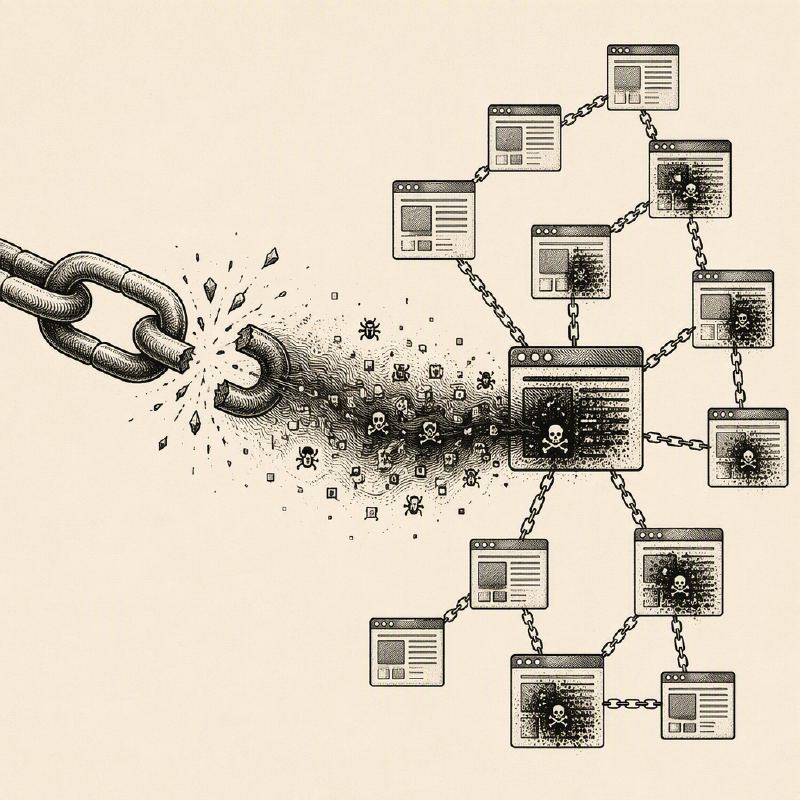
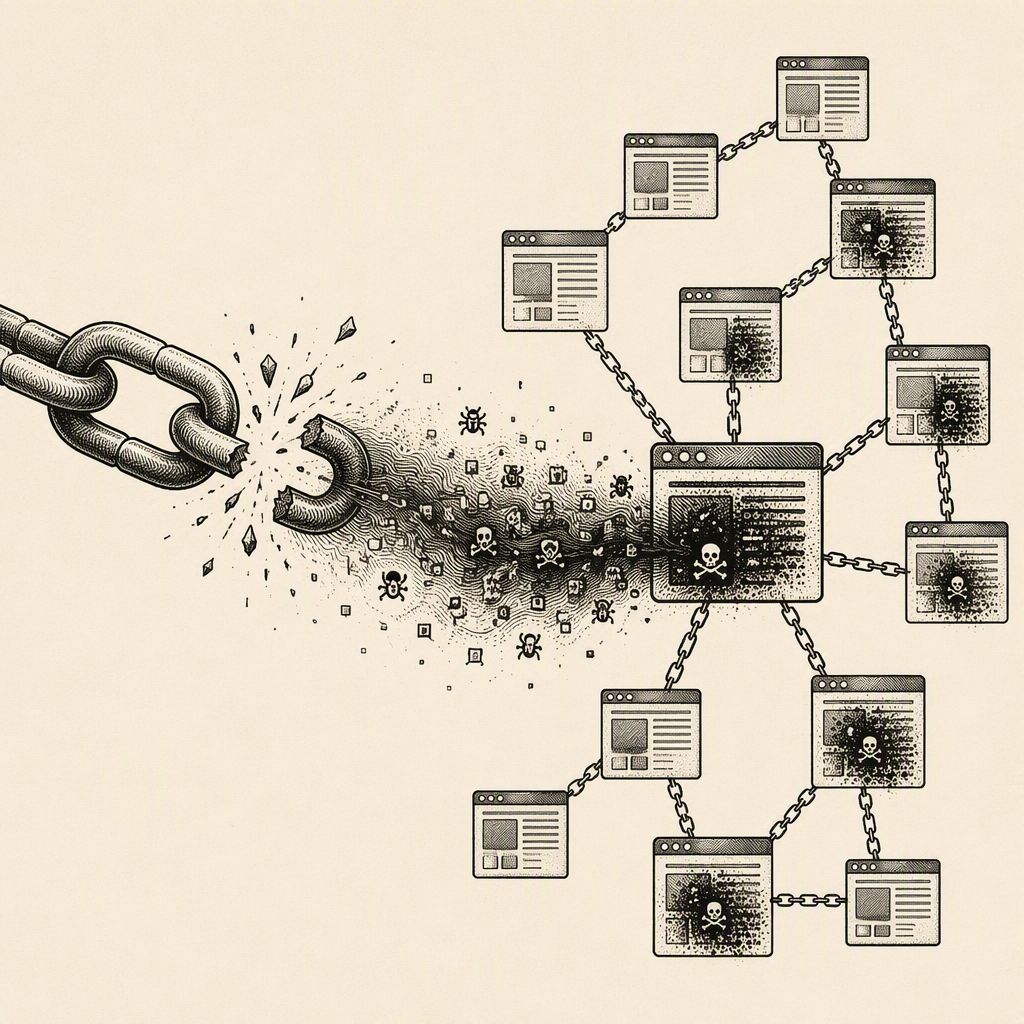
A sophisticated supply chain attack targeting Brevo, a widely used email and marketing platform, has resulted in the compromise of over 100,000 WordPress websites. Attackers successfully injected malicious JavaScript into Brevo's services, which then propagated to customer sites that utilized Brevo's tracking scripts, chat widgets, or sign-up forms. This incident, which occurred on September 14, 2026, highlights the significant risks associated with the interconnectedness of modern web infrastructure.
The attack unfolded in two primary phases. For logged-in WordPress administrators, the malicious script attempted to install a plugin, likely a backdoor, directly through their active session. This method would have provided attackers with persistent, covert access to the affected websites. For regular visitors to compromised sites, the attackers deployed a deceptive "ClickFix" overlay. This prompt mimicked a human verification step, instructing users to copy and paste a command into their system's command line, effectively tricking them into executing malware without exploiting any browser vulnerabilities.
Researchers at Sansec, who investigated the incident, traced the altered scripts across Brevo's owned services and customer integrations. The malicious code was served between 16:05:18 and 20:12:53 UTC on September 14. The compromised components included Brevo's website tracker, chat widget, and hosted forms. The attack's reach was amplified by the fact that these components are embedded across a vast number of websites, turning a single point of compromise into a widespread distribution vector.
The ClickFix malware campaign is particularly concerning due to its reliance on social engineering. By presenting a seemingly legitimate verification process, attackers leveraged user trust and a familiar web interaction pattern to persuade victims into performing the final, malicious step themselves. This approach bypasses traditional security measures that focus on detecting malicious downloads or exploits.
While the initial reports suggested a limited number of compromised Brevo accounts, Sansec's findings indicate a broader compromise of Brevo's shared delivery infrastructure, potentially through their Cloudflare environment. This allowed attackers to alter DNS records and modify responses across related domains, impacting sites that had no direct account compromise. The malicious domains associated with the attack, such as cdn9.sendibt1.com and cdn2.sendibt1.com, were observed to stop resolving by September 15, and the affected code at the origin was reportedly cleaned.
However, the lingering threat of cached copies of the malicious scripts and compromised websites remains. Site owners who used the affected Brevo components are advised to meticulously review their web server logs for suspicious upload and activation requests, particularly on September 14. They should also scrutinize their installed WordPress plugins for any unauthorized additions or modifications, as malicious plugins may attempt to hide from standard administrative views.
For visitors who executed the command prompted by ClickFix, a thorough antivirus scan of their devices is strongly recommended, along with monitoring for any unusual system behavior. Security teams are urged to preserve relevant logs, reset privileged accounts where necessary, and conduct comprehensive integrity checks on their web infrastructure. The incident underscores the critical need for continuous monitoring of third-party JavaScript, restricting administrative access, and implementing rapid integrity checks following any supplier-related security event.
This supply chain attack on Brevo serves as a stark reminder of how a single vulnerability or compromise in a trusted service can cascade into a massive security incident, affecting thousands of businesses and their users. The dual-pronged approach, targeting both administrators with backdoors and visitors with social engineering, demonstrates a versatile and dangerous attack strategy.
This new report indicates that the supply chain attack on Brevo involved the deployment of a malicious Cloudflare worker, which was enabled by a compromised API key. This worker was responsible for injecting harmful scripts into approximately 100,000 websites, underscoring the critical importance of securing API keys and managing third-party service integrations.