
BigDiskBuster Technique Allows Malware to Evade Microsoft Defender Updates
A new proof-of-concept technique named 'BigDiskBuster' enables malware to run undetected by Microsoft Defender by preventing its updates and disabling real-time protection without triggering alerts.
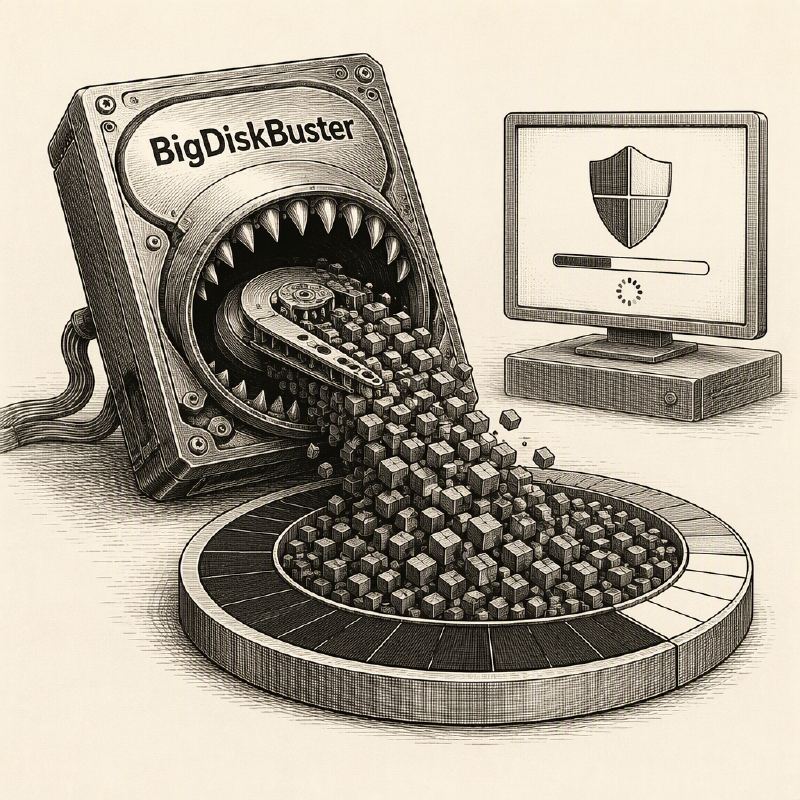
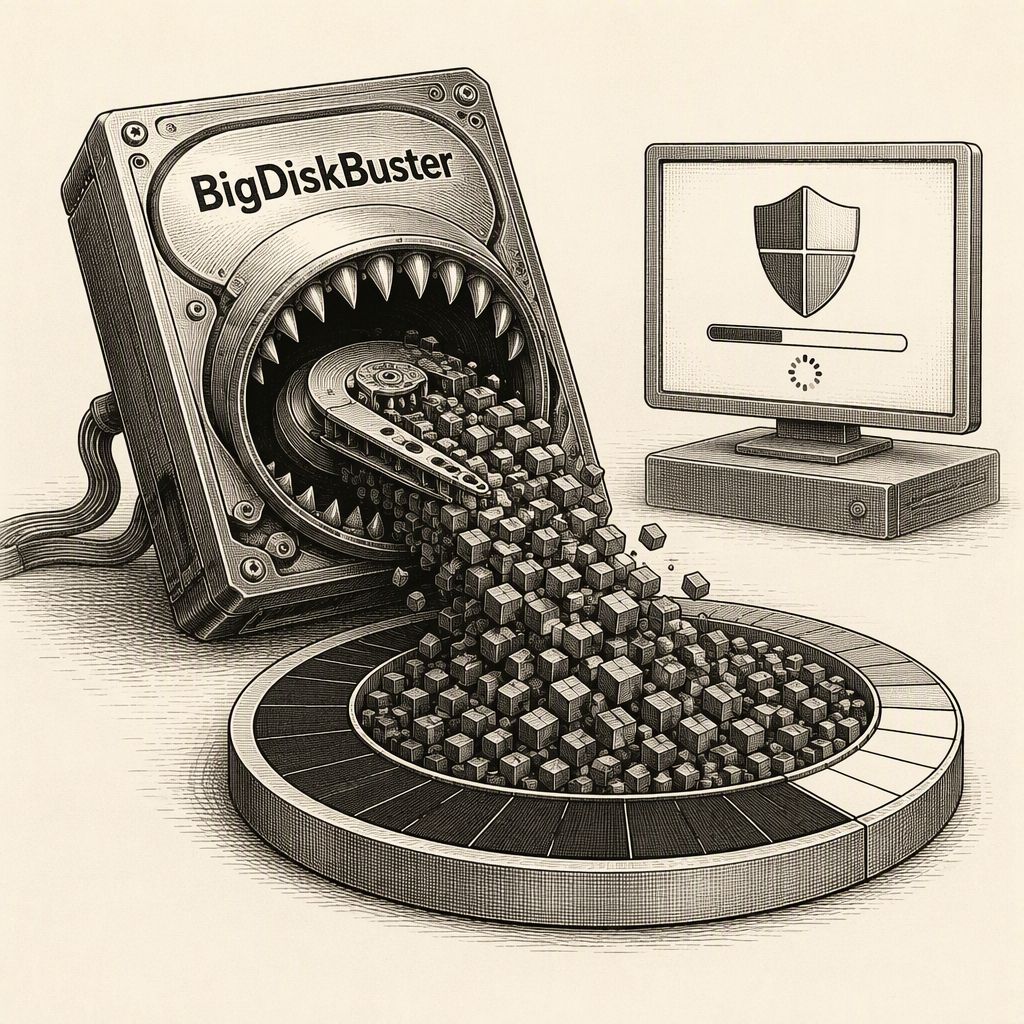
A novel proof-of-concept (PoC) technique dubbed 'BigDiskBuster' has emerged, allowing malware to operate stealthily by preventing Microsoft Defender from receiving critical updates. Developed by security researcher Abdelhamid Naceri and further analyzed by LevelBlue, this method circumvents Defender's update mechanisms without exploiting a specific vulnerability, creating a silent window for undetected malicious activity.
The core of the BigDiskBuster technique involves monitoring the system's primary volume, typically C:\, for Defender update processes. When an update attempt is detected, the PoC dynamically creates a hidden file that consumes nearly all available free disk space. This artificial scarcity effectively halts the Defender update process, as it cannot complete its download or installation.
Once the update fails due to the lack of disk space, Defender initiates a cleanup of its staging directories, thereby freeing up the claimed space. BigDiskBuster then waits for the next scheduled Defender update attempt and repeats the cycle. Crucially, during this entire process, Defender's core service remains active, and its real-time protection capabilities appear to be functioning normally, masking the fact that the endpoint is no longer receiving the latest threat intelligence.
Researchers from LevelBlue successfully reproduced the PoC, confirming its ability to create a "silent detection gap." Their testing demonstrated that BigDiskBuster can operate effectively even under a standard user account, making it accessible to a wide range of attackers. The technique combines several mechanisms, including raw device handles, relative file opens, recursive volume watching, and oversized allocations, all orchestrated to disrupt the update process.
While BigDiskBuster does not disable Defender outright or trigger obvious product failures, its impact lies in extending the lifespan of existing malware on an infected system. By preventing Defender from updating its detection signatures, attackers can ensure that their tools remain undetected for longer periods, evading newly developed countermeasures.
Microsoft has stated that Microsoft Defender Antivirus includes detections and preventions against this PoC. The company advises customers to ensure their security intelligence and platform updates are current. Although there is no specific CVE or advisory for BigDiskBuster, the researchers noted that indicators of compromise can be observed at the I/O layer. Unusual handle activity, repeated Defender update failures (particularly error code 0x80070643), and abnormal disk allocation behaviors can signal that this technique is being employed.
LevelBlue's analysis highlights the importance of monitoring not just whether security software is running, but whether its protection content is actively being updated. The BigDiskBuster PoC serves as a stark reminder that even seemingly robust security solutions can be circumvented through clever manipulation of system processes, underscoring the need for continuous vigilance and layered security approaches.