
Axoflow AxoDetect Aims to Reduce SIEM Costs by Processing Detections in the Data Pipeline
Axoflow has launched AxoDetect, a new component that processes security detection rules directly within the data pipeline before logs reach the SIEM, aiming to significantly cut SIEM costs.
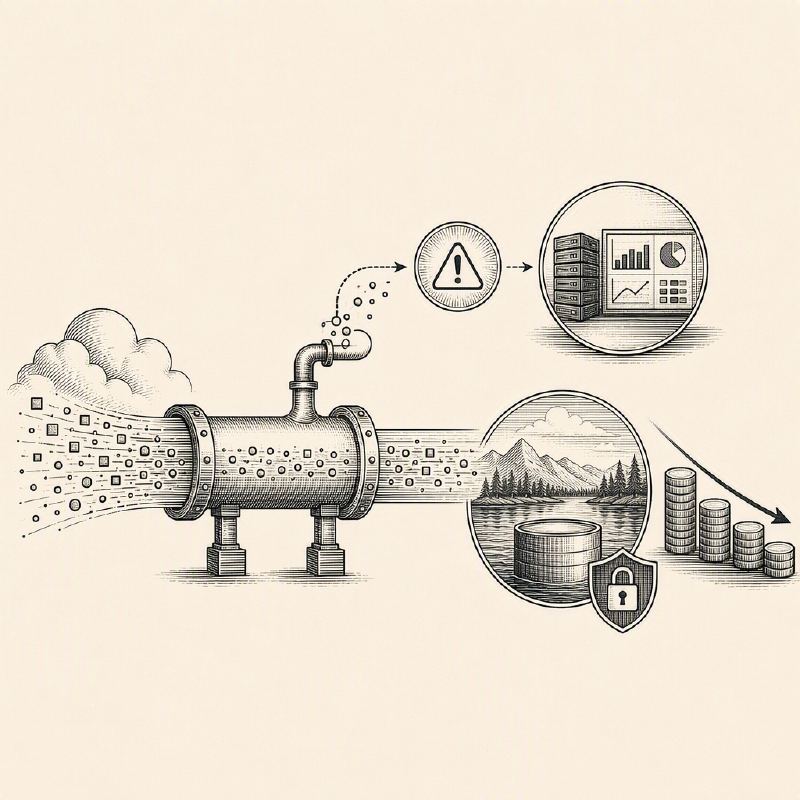
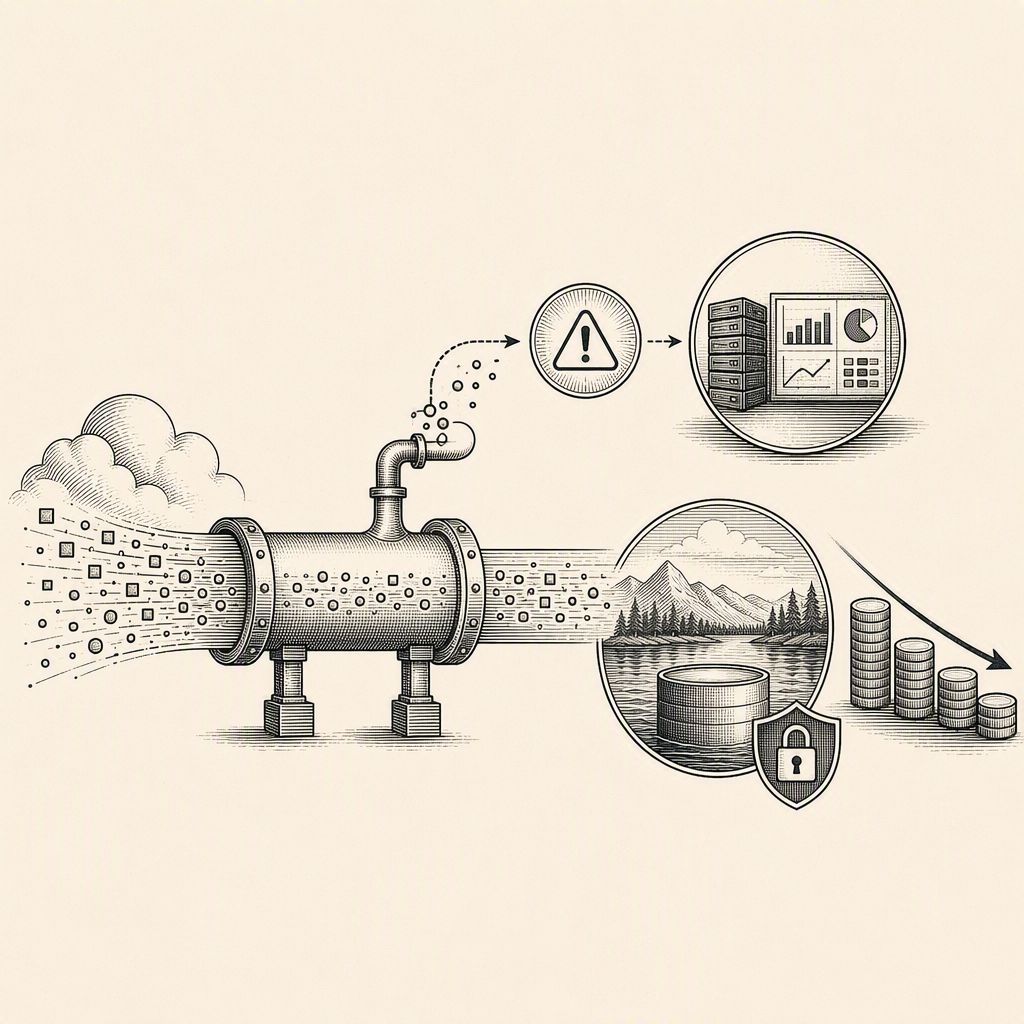
Axoflow has introduced AxoDetect, a new component designed to revolutionize how security detections are handled by processing them directly within the data pipeline, before logs are ingested into a Security Information and Event Management (SIEM) system. This innovative approach aims to drastically reduce the operational costs associated with SIEMs, which are often burdened by the expense of ingesting and storing vast amounts of raw log data.
Announced during Splunk .conf26, AxoDetect allows organizations to run their existing detection rules, including those written in the open Sigma format, on normalized data streams in real-time. This means that alerts generated by these rules are sent to the SIEM for analyst workflow and investigation, while the full, raw log data is sent to AxoLake, Axoflow's low-cost security data lake. This separation allows the SIEM to function primarily as a Security Operations (SecOps) workflow engine, rather than an expensive log management solution.
Detection engineers often face challenges with the sheer volume of data and the cost of SIEM ingestion. AxoDetect addresses this by ensuring that detections are applied to cleaner, more manageable data earlier in the process. This not only saves money but also improves the efficiency of detection by reducing noise and false positives that can arise from raw, unparsed data. The platform also provides crucial visibility into data sources and the performance of detection rules, a capability that has historically been fragmented across different teams and tools.
Early adopters of AxoDetect have reported substantial savings and performance improvements. One global industrial company reportedly cut its SIEM costs by 50% and reduced its mean time to resolution (MTTR) by 85%. Similarly, a government agency achieved an 80% reduction in data volume and an 85% decrease in its infrastructure footprint. These results highlight the tangible benefits of shifting detection closer to the data source.
Balázs Scheidler, CEO and co-founder of Axoflow and creator of syslog-ng, emphasized the paradigm shift: "The SIEM became the industry's most expensive data swamp because it was the place where we kept all of our raw data. That constraint is gone. Detection belongs in the data layer, on normalized data, before the ingest meter starts. Keep your workflow in the SIEM. Send the alerts, but not your entire data estate."
Axoflow's vision extends to running the full detection lifecycle within the data layer, a capability that is expected to roll out in the coming months. The company, known for its origins with syslog-ng, positions itself as an autonomous security data layer that handles data collection, processing, routing, storage, and management, now with in-stream detection capabilities.
The platform promises to deliver significant improvements in investigation speed, SIEM spend reduction, and pipeline maintenance through AI-based autonomy, moving beyond simple chatbot functionalities. This move signifies a broader trend in the cybersecurity industry towards more efficient and cost-effective data management and threat detection strategies.
AxoDetect's launch addresses a critical pain point for many organizations struggling with escalating SIEM costs and the complexity of managing large volumes of security data. By enabling detections to run in the pipeline, Axoflow offers a compelling alternative that prioritizes cost savings without compromising security coverage.