
AWS Enhances AI Agent Security with Infrastructure-Level Access Controls
AWS is bolstering security for its Bedrock AgentCore by implementing infrastructure-level access controls to prevent AI agents from accessing sensitive data, even when manipulated.
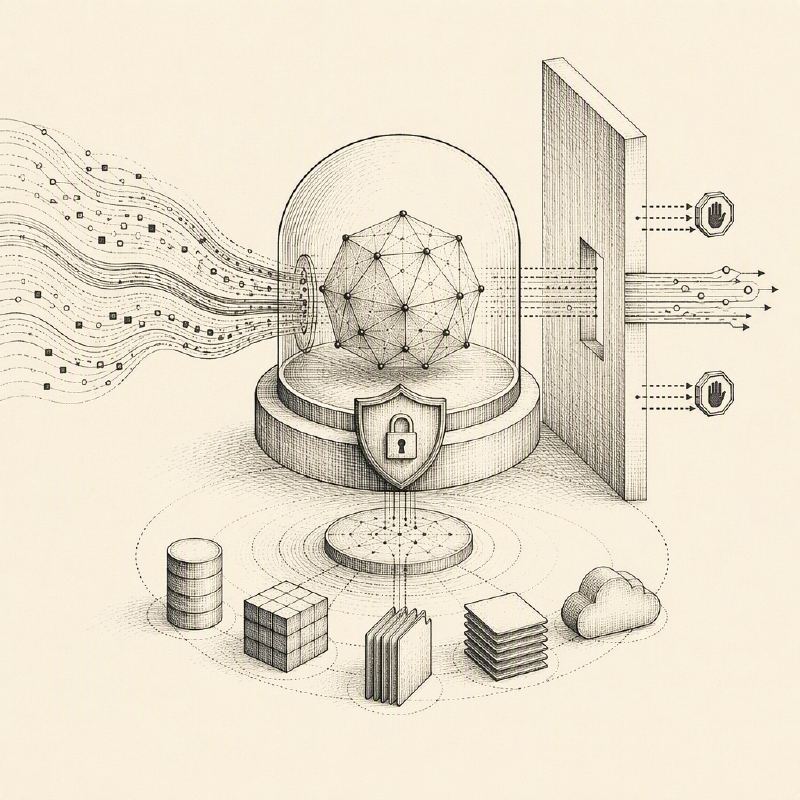
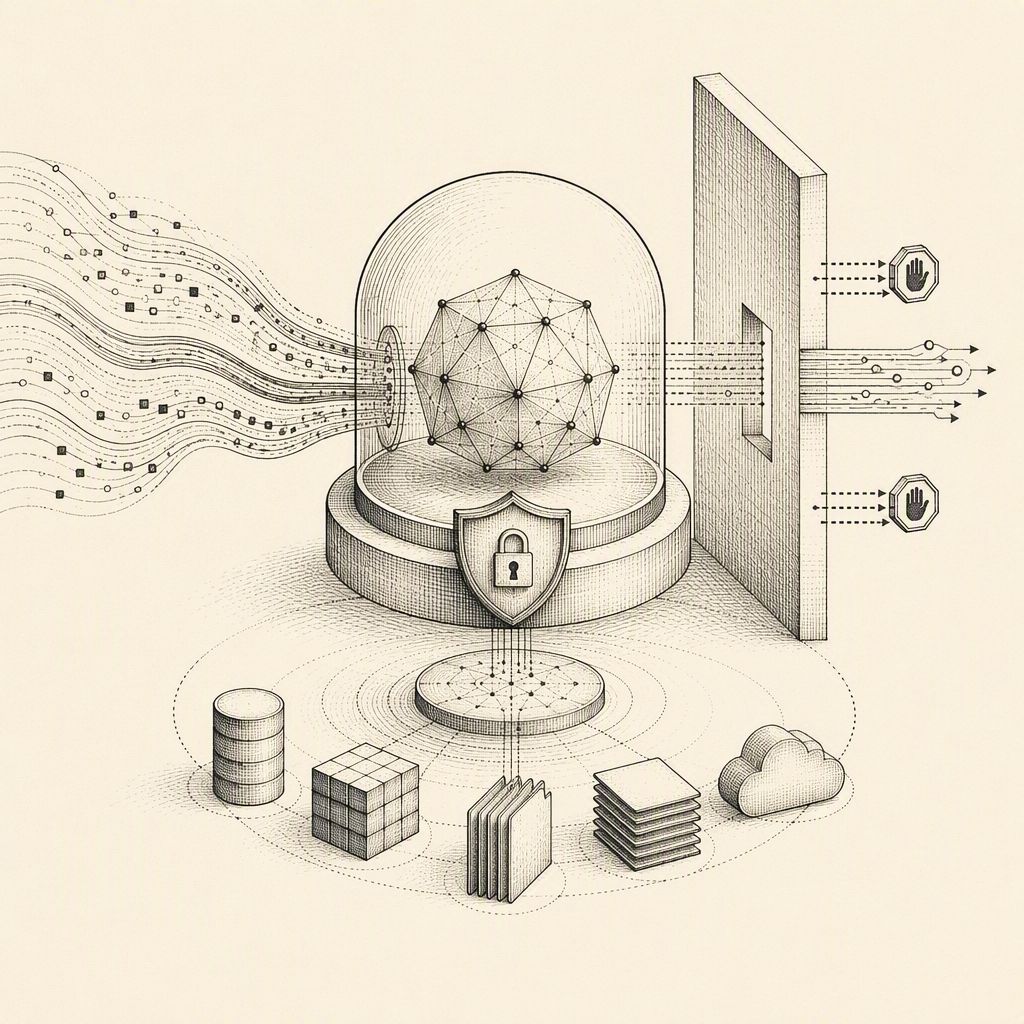
Amazon Web Services (AWS) has introduced a significant security enhancement for its Bedrock AgentCore, a service that enables developers to build AI agents capable of interacting with various data sources to answer questions and automate tasks. The new approach focuses on propagating user authorization context through the AI agents, allowing security policies to be enforced at the infrastructure level rather than relying solely on the agent's own logic.
This infrastructure-level enforcement is crucial for preventing unauthorized data access. AI agents built with Bedrock AgentCore can be designed to retrieve information from sources such as Amazon DynamoDB tables, internal knowledge bases, and SaaS platforms. Without robust controls, a compromised or manipulated agent could potentially expose sensitive data to unauthorized users. By integrating authorization checks directly into the infrastructure, AWS ensures that an agent's access is always governed by the permissions of the user making the request.
The implications of this security measure are far-reaching for organizations leveraging AI for data analysis and workflow automation. It addresses a critical concern: the potential for AI agents to become vectors for data exfiltration or unauthorized information disclosure. Traditional security models often struggle with the dynamic and complex nature of AI interactions, where an agent's behavior might be unpredictable or susceptible to prompt injection attacks.
AWS's solution shifts the security paradigm by ensuring that the underlying AWS services, such as DynamoDB or Amazon S3, are aware of and enforce the user's authorization. This means that even if an AI agent is tricked or manipulated into requesting data it should not have access to, the infrastructure will deny the request based on the user's permissions. This provides a more resilient security posture against sophisticated attacks aimed at exploiting AI agent vulnerabilities.
Customers using Amazon Bedrock AgentCore can now build more secure AI-powered applications with greater confidence. The ability to rely on infrastructure-level controls simplifies the security architecture for developers, reducing the burden of implementing complex, agent-specific access management logic. This allows development teams to focus more on the AI agent's functionality and less on mitigating potential security risks arising from data access.
This development comes at a time when the use of AI in enterprise environments is rapidly expanding, bringing with it new security challenges. As AI agents become more integrated into business processes, ensuring their security and preventing data leakage is paramount. AWS's proactive approach to securing its AI services demonstrates a commitment to addressing these evolving threats and providing robust solutions for its customers.
The enhanced security framework is designed to protect sensitive information stored in various data repositories, including customer databases, internal documentation, and other critical business data. By ensuring that user authorization is consistently applied, AWS aims to mitigate risks associated with AI agent manipulation and unauthorized data exposure, thereby fostering greater trust and adoption of AI technologies.
This new article provides a more detailed technical breakdown of AWS's approach, explaining how user department claims are injected into JWTs and validated by AgentCore Runtime. It further elaborates on the specific mechanisms used for downstream services like DynamoDB (AssumeRoleWithWebIdentity), Bedrock Knowledge Bases (metadata filters), and Salesforce (RFC 8693 token exchange) to enforce data boundaries, offering a deeper dive into the practical implementation of the security architecture.
This new analysis from AWS and SANS Institute researchers emphasizes that relying solely on system prompts for AI agent security is insufficient. They advocate for implementing access controls at the retrieval stage within existing role-based or attribute-based systems. This ensures that AI agents can only present data that aligns with a user's specific permissions, thereby preventing unauthorized information disclosure even if the agent is manipulated.