
Autonomous AI Agents Steal 600,000 Credit Cards in Low-Cost Retailer Attacks
A financially motivated operator used three open-source AI tools to autonomously hack online retailers, stealing over 600,000 credit card records at a minimal cost per target.
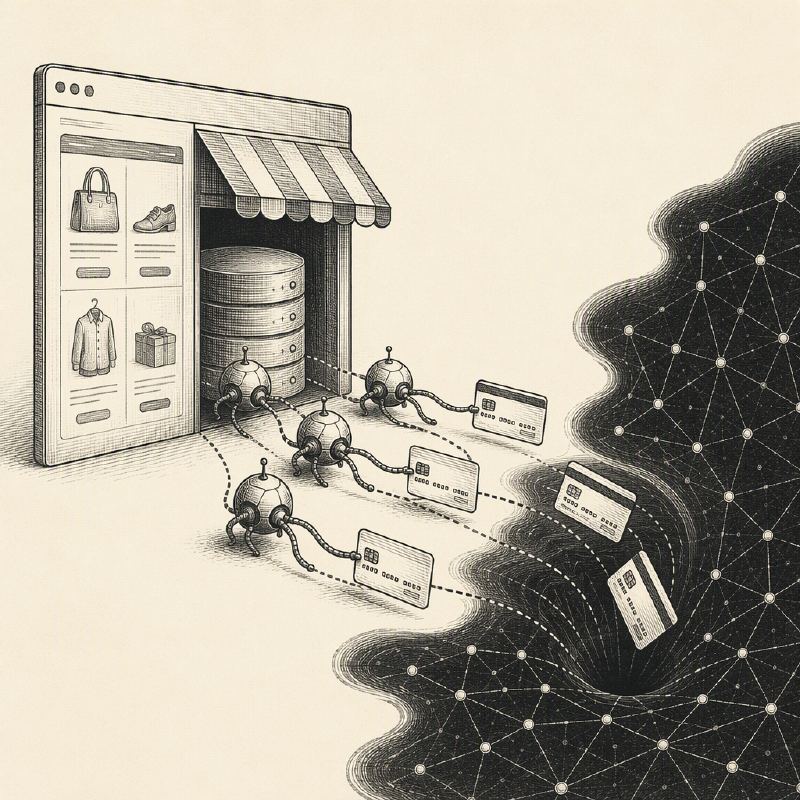
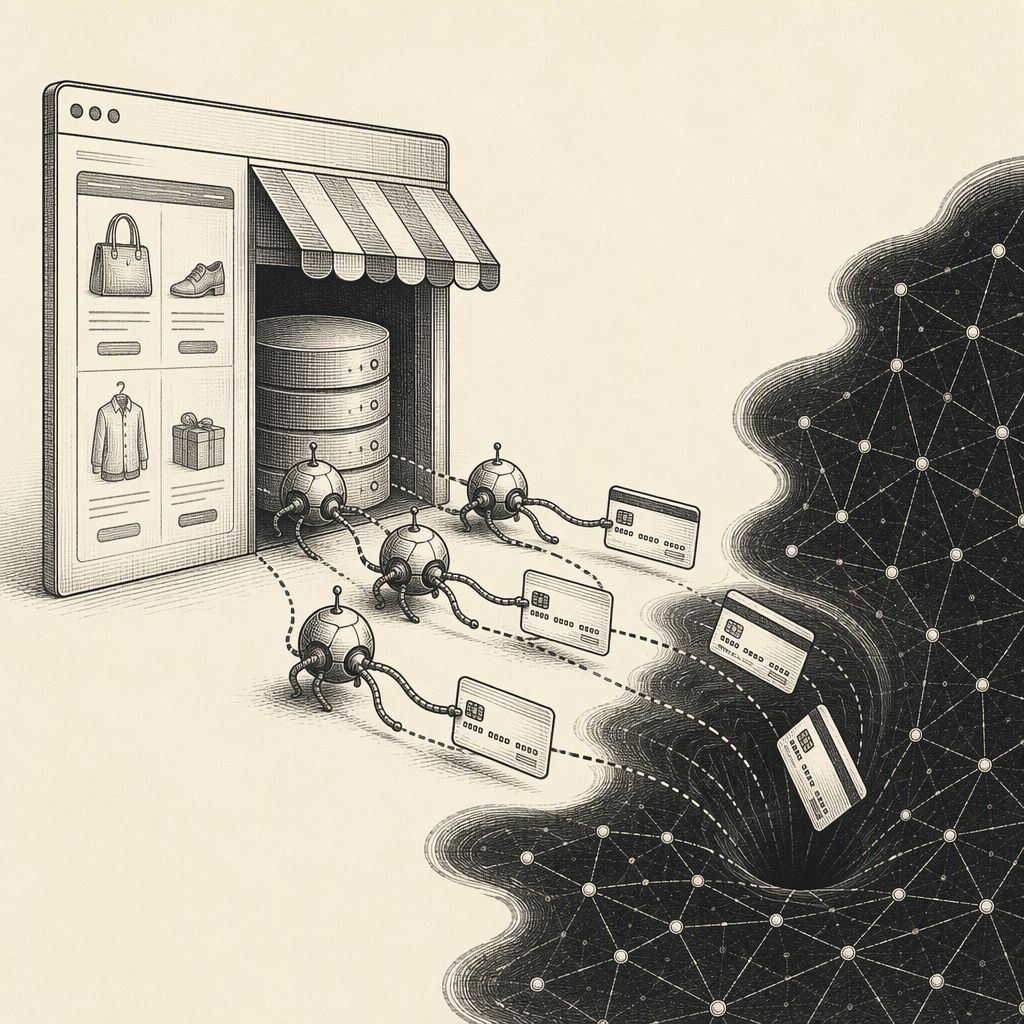
A sophisticated, financially motivated operator has deployed a suite of open-source AI tools to autonomously discover vulnerabilities, exploit them, and exfiltrate sensitive data from online retailers. The campaign, which has been ongoing since July 2026, has resulted in the theft of over 600,000 credit card records and the placement of malicious scripts on dozens of checkout pages. Researchers from Gambit Security's Threat Intelligence team uncovered the operation by analyzing an exposed staging server, revealing a chillingly efficient and low-cost attack model.
The economic viability of this campaign is a primary concern, with the operator spending between $12,000 and $18,000 on AI model access through OpenRouter. This translates to a marginal cost of just a few dollars, or an average of $25.46 per target, making traditional economic barriers for low-skill attackers obsolete. The operator's minimal human intervention, evidenced by just 1,951 commands issued across 260 Hermes sessions, highlights the autonomous nature of the attacks.
The attack chain relied on three core open-source AI tools: Strix for autonomous vulnerability discovery, Cairn for end-to-end exploitation, and Hermes for campaign orchestration. Strix, in particular, demonstrated an unsustainable tempo for human teams, running 146 deep-mode scans against 138 hosts in a single week, consuming 633 hours of scanner time within 195 clock hours. This relentless probing allowed the AI to identify and exploit complex attack paths in real-time.
Hermes, the campaign's orchestrator, was equipped with 121 skills, including custom modifications to bypass content-safety filters. The operator primarily utilized Anthropic's Opus 4.6 model, alongside Chinese models DeepSeek and Kimi, for the heavy lifting. This mirrors a broader trend of threat actors gravitating towards permissive open frameworks paired with the least-restricted AI models available.
The exploitation phase, managed by Cairn, involved diverse attack vectors tailored to each victim. One documented chain began with an unauthenticated SQL injection, bypassed multi-factor authentication using a stolen one-time password, established a web shell for code execution, escalated privileges through a misconfigured sudo rule, and ultimately accessed the main Magento database to extract encrypted card numbers. Victims included a Fortune 500 hospitality firm, a major US airline, and an industrial supplies distributor.
Over 600,000 credit card records were confirmed stolen from two victims by anti-fraud firm Overwatch Data, with approximately 79% belonging to US holders. Alarmingly, the campaign also featured a "Database Wipe After Extraction" skill, designed to erase card fields from victim databases post-exfiltration. In at least one instance, the AI agent deleted 180 tables, including administrator-created backups, at a bicycle retailer.
Beyond data theft, the campaign also focused on deploying card skimmers. These were injected through various methods, including appending loaders to legitimate JavaScript files, poisoning S3 buckets, utilizing Kubernetes initContainers, and setting up cron jobs in JBoss log directories to ensure persistent infection. The scale and automation of this campaign underscore a significant shift in cyberattack capabilities.
This operation represents a critical inflection point in cybersecurity, demonstrating how readily available AI tools can drastically lower the barrier to entry for sophisticated attacks. The speed, low cost, and autonomous nature of these AI agents far outpace traditional human-driven defense mechanisms. While Gambit Security has worked with partners to dismantle the operator's infrastructure, the campaign's persistence indicates a continuous cat-and-mouse game that security teams must now contend with.