
ANY.RUN Enhances Malware Analysis with AI for Complex Phishing and Threat Intelligence
ANY.RUN's AI-assisted sandbox now automates multi-stage phishing analysis, including CAPTCHA and OAuth flows, accelerating SOC response and threat intelligence correlation.
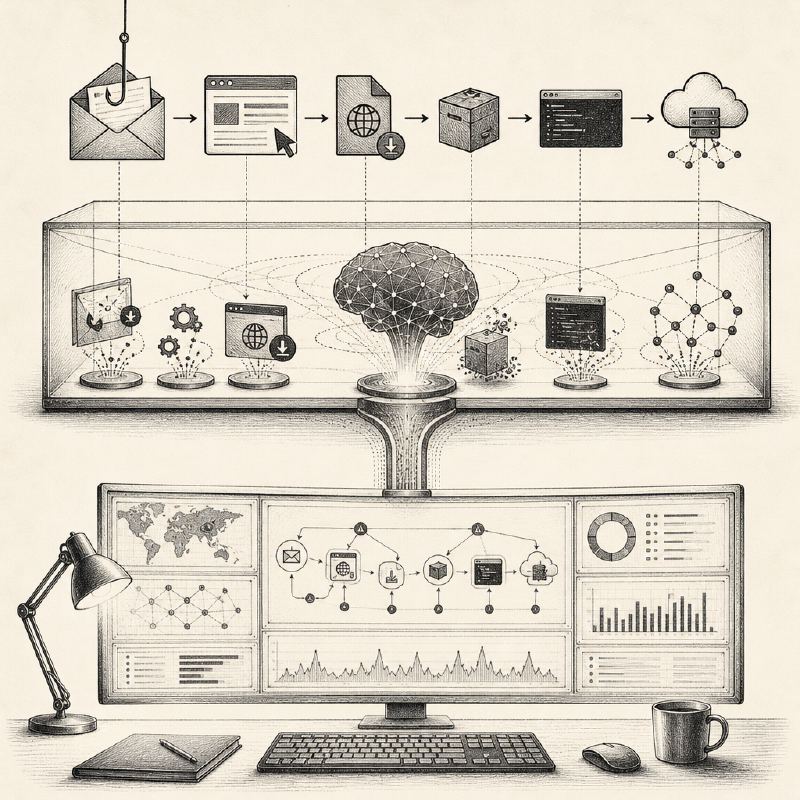
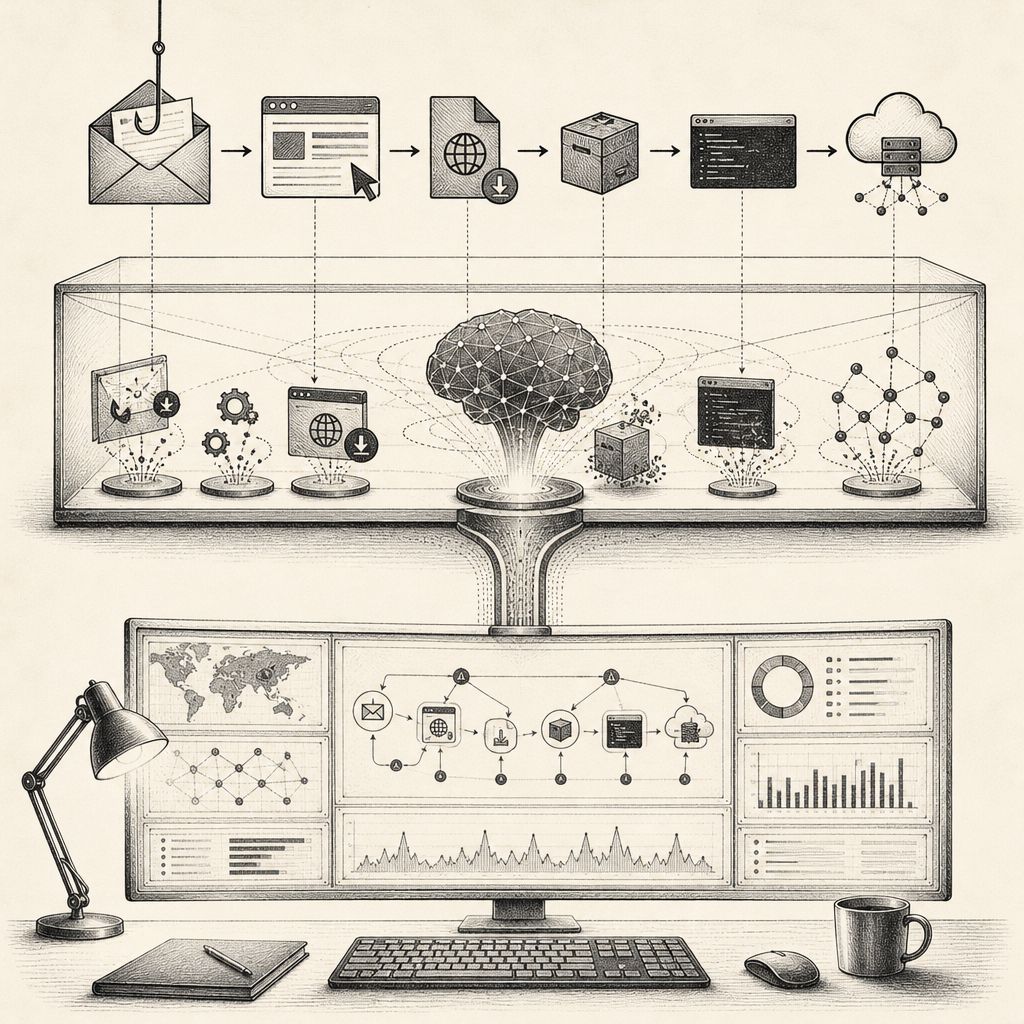
Security operations centers (SOCs) often face lengthy investigations when analyzing phishing attacks that involve multiple stages and user interactions. Traditional sandboxing methods can struggle with complex attack chains that hide malicious activity behind CAPTCHAs, OAuth flows, or other interactive elements. ANY.RUN has introduced an AI-assisted sandbox designed to automate these complex analyses, significantly speeding up the process for security analysts.
The platform's AI-assisted Automated Interactivity feature allows the sandbox to navigate through intricate attack progressions. For instance, an analysis starting with a PDF hosted on a legitimate platform like acrobat.adobe.com can automatically proceed through embedded links, solve CAPTCHA challenges, and even capture activity from subsequent Microsoft OAuth phishing flows. This automation ensures that analysts don't miss crucial steps hidden within the attack chain, providing a more comprehensive view of the threat.
Beyond automated execution, ANY.RUN emphasizes the importance of interactive analysis. Analysts retain the ability to pause the sandbox at any stage, inspect suspicious behaviors, or explore alternative attack paths without initiating a new investigation. This blend of automation and interactivity is particularly valuable for phishing campaigns that rely on user engagement to reveal their true malicious intent, allowing for deeper scrutiny of the hidden elements.
A significant advancement highlighted is the new Related Threat Context capability, which integrates threat intelligence directly into the analysis workflow. This feature automatically surfaces over 70 related sandbox analyses alongside suspicious indicators, enabling analysts to quickly identify connections between seemingly isolated incidents. By pivoting from a single finding to previous investigations, teams can uncover shared infrastructure, such as domains like slybee[.]com, and link them to known campaigns.
This threat intelligence correlation is crucial for understanding the broader scope of an attack. ANY.RUN's Threat Intelligence Lookup reveals associated IP addresses, URLs, network connections, and threat classifications, directly linking the suspicious infrastructure to campaigns like SkyW4lker. Such insights empower analysts to conduct more effective threat hunting, check SIEM and EDR logs for wider compromise, and improve overall detection engineering.
To further streamline SOC workflows, ANY.RUN now offers SOC-ready Tier 1 reports generated with AI assistance. These reports combine technical investigation evidence with an AI Summary explaining observed behavior and potential impact, alongside AI Recommendations for investigation and response steps, including relevant MITRE ATT&CK context. While not replacing analyst judgment, these reports provide a documented starting point for Tier 1 analysts and essential information for Tier 2 escalation.
The integration of AI in malware analysis, as demonstrated by ANY.RUN, is transforming how security teams respond to sophisticated threats. By automating complex interactions, correlating findings with extensive threat intelligence, and generating actionable reports, these tools enable faster detection, more efficient investigations, and ultimately, stronger defenses against evolving cyberattacks.