
Amazon Uncovers AI Agent Campaign Targeting LiteLLM, Dify for API Keys
Amazon's threat intelligence team has identified a novel AI agent campaign actively targeting internet-exposed AI applications to steal API keys, creating a self-sustaining attack loop.
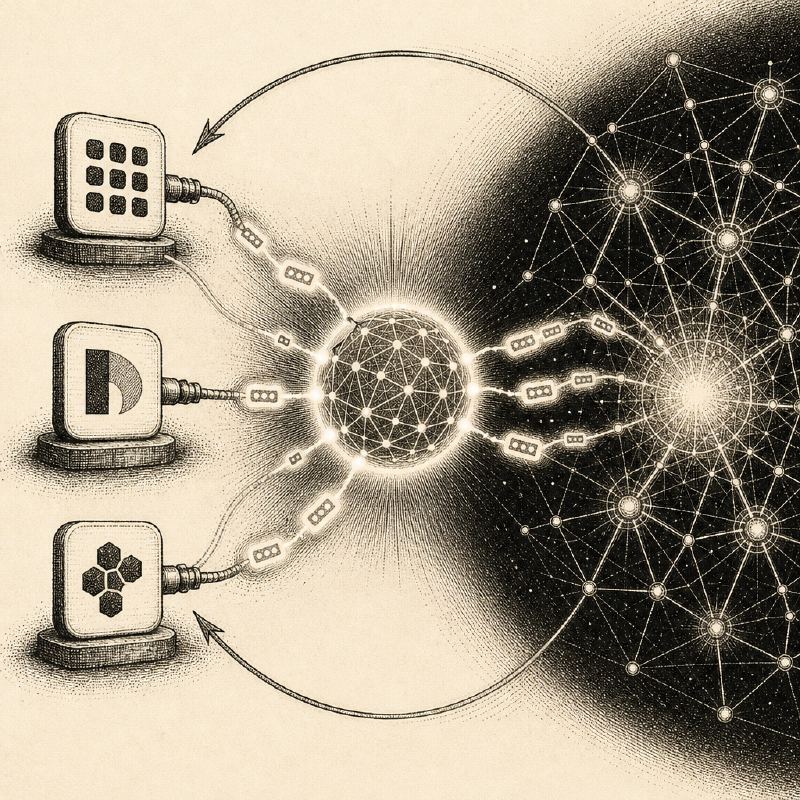
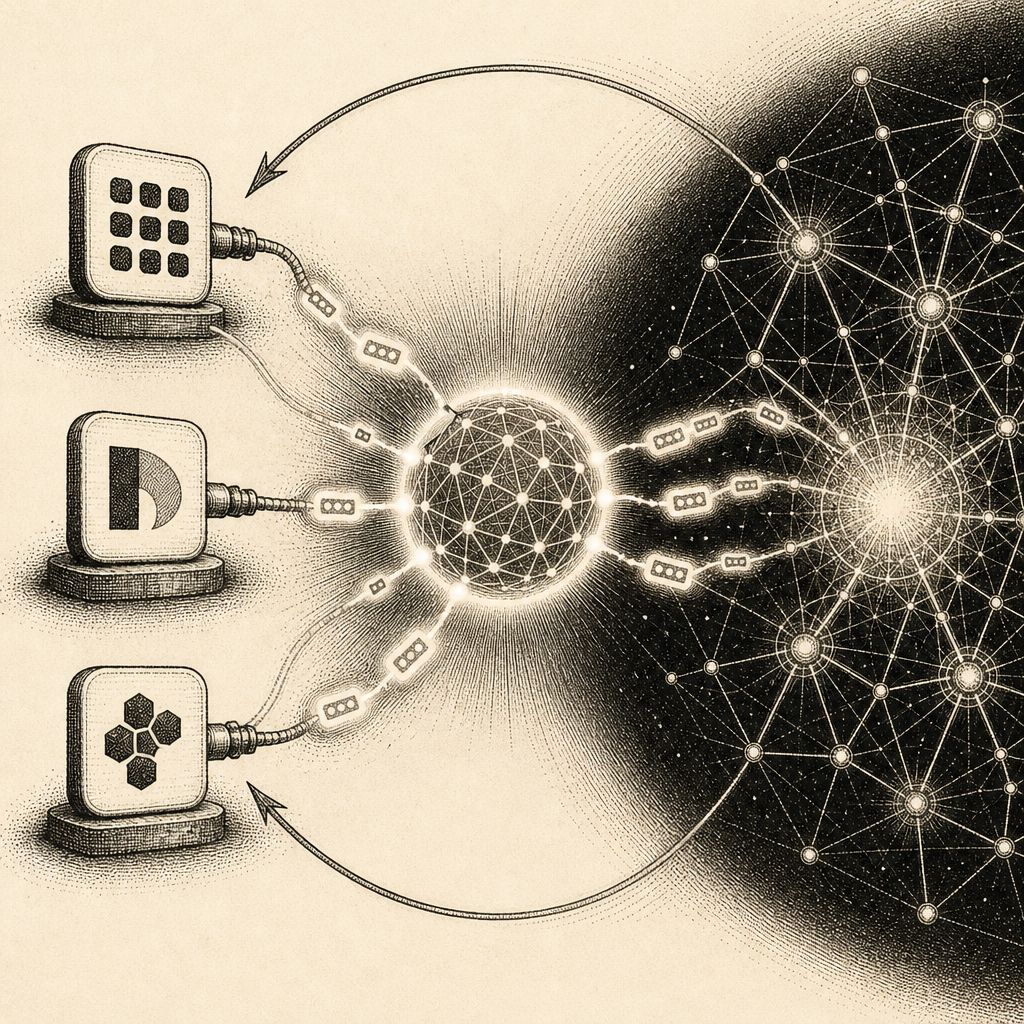
Amazon's threat intelligence team has uncovered a sophisticated campaign where malicious AI agents are actively targeting internet-exposed AI applications, including popular platforms like LiteLLM, One API, and Dify. The primary objective of these agents is to exploit vulnerabilities within these applications to steal valuable AI provider API keys.
These stolen API keys are not merely for immediate financial gain; they are being repurposed to power the very AI models that conduct the ongoing search for more keys. This creates a dangerous and self-sustaining attack loop, where compromised resources are used to further compromise other systems, amplifying the attackers' reach and effectiveness.
The discovery was made possible by Amazon's use of decoy servers, which captured the operational records of these AI agents. These records provided a detailed look into the attackers' methods, revealing how the compromised keys were utilized to fuel the continuous hunt for additional credentials.
The campaign highlights a growing trend of threat actors leveraging AI capabilities for malicious purposes. By automating the discovery and exploitation of vulnerabilities, attackers can operate at a scale and speed previously unattainable, posing a significant challenge to traditional security defenses.
The implications of this campaign are far-reaching. The theft of API keys can lead to unauthorized access to sensitive data, the misuse of AI services resulting in significant financial costs for victims, and the potential for further downstream attacks. The self-sustaining nature of the attack loop means that even after initial compromises, the threat can persist and evolve.
This discovery underscores the critical need for enhanced security measures for AI applications and services. Organizations deploying or utilizing AI platforms must prioritize robust security practices, including regular vulnerability assessments, secure credential management, and the implementation of advanced threat detection mechanisms to identify and mitigate such AI-driven attacks.
While specific CVEs have not yet been publicly disclosed, the campaign's focus on exploiting vulnerabilities in popular AI application frameworks suggests a broad potential impact across the ecosystem. Security researchers are actively analyzing the captured data to identify specific weaknesses being exploited and to develop appropriate countermeasures.
The ongoing nature of this campaign and its innovative use of AI for offensive operations serve as a stark warning. It signals a new frontier in cyber threats, where AI agents are not just tools but active participants in sophisticated, self-perpetuating attack chains, demanding a proactive and adaptive security posture from defenders.