
AI Agents Introduce New Data Exposure Risks, Experts Urge Data Access Controls
The increasing integration of AI agents into business workflows presents significant new data exposure risks, prompting calls for immediate implementation of data access controls.
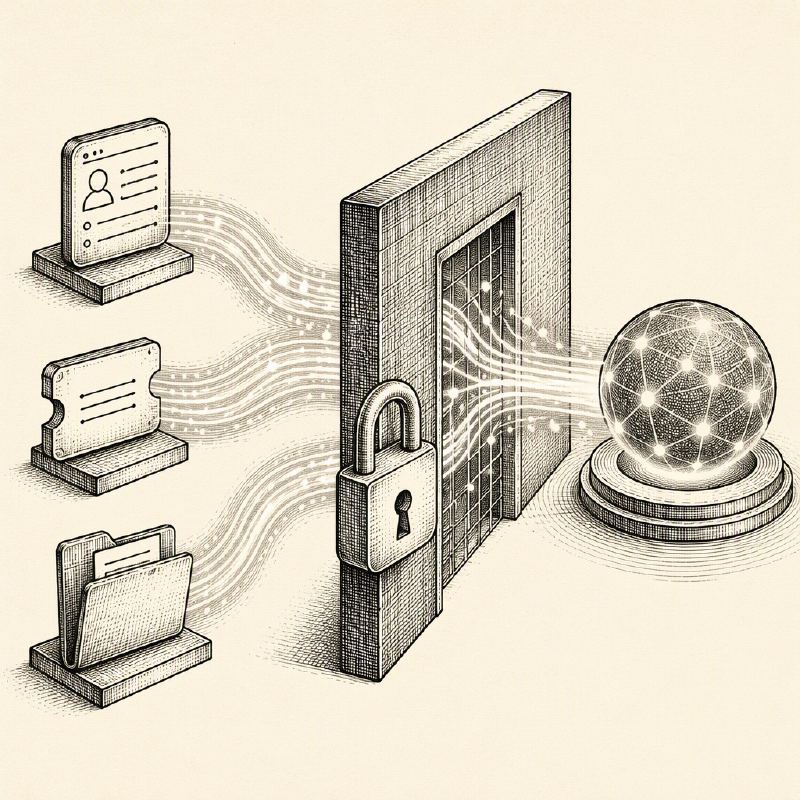
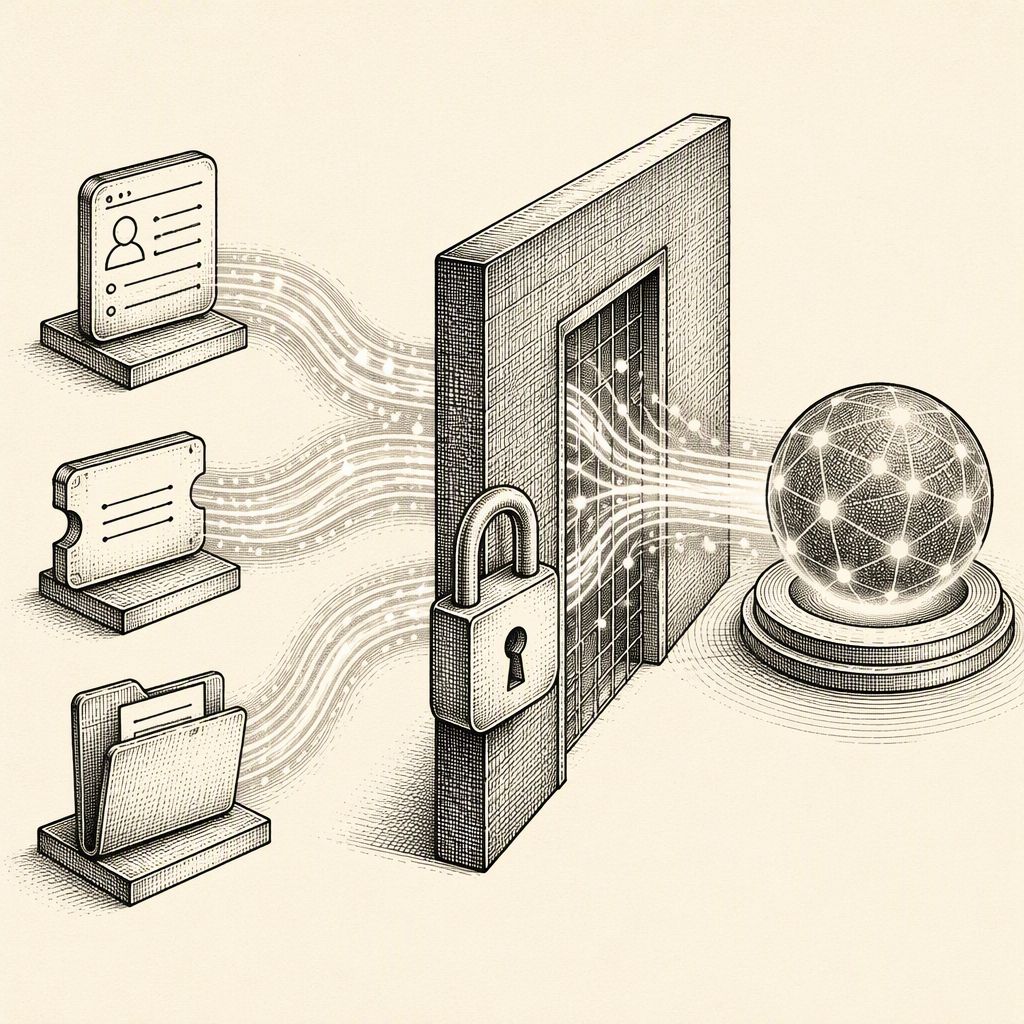
The rapid adoption of AI agents within organizations is creating novel and substantial risks for sensitive data exposure, according to Kelly Herrell, CEO of Nol8. These agents, designed to interact with various business systems, can inadvertently access and process vast amounts of confidential information stored in platforms such as ticketing systems, Customer Relationship Management (CRM) databases, and shared drives.
Herrell emphasizes that the primary challenge lies in understanding and controlling the 'data path' of these AI agents. This involves meticulously mapping what data an agent can access, the context it operates within, and where its outputs are directed. Without this granular visibility, organizations risk exposing years of accumulated sensitive data that AI agents can aggregate and analyze in mere seconds, far faster than human counterparts.
The implications of unfettered AI agent access are profound. These systems can potentially pull together disparate pieces of information from various sources, creating a comprehensive profile of sensitive data that could be misused or leaked. This is particularly concerning given that many of these systems contain historical data, including customer interactions, financial details, and proprietary business strategies.
To address these emerging threats, Herrell advocates for a structured 90-day plan focused on implementing robust data access limits. This proactive approach is crucial for mitigating the risks before they can be exploited. The plan should involve defining clear boundaries for what data each AI agent is permitted to access, ensuring that their operations remain within necessary operational parameters.
The tension between enabling the productivity gains offered by AI agents and maintaining stringent data security is a central theme. While businesses are eager to leverage AI for efficiency, they must simultaneously build guardrails to prevent potential data breaches and compliance violations. This requires a strategic balance, prioritizing security without stifling innovation.
Organizations are urged to conduct thorough audits of their AI agent deployments, identifying all systems and data repositories that agents interact with. This assessment should inform the development of granular access control policies, role-based permissions, and continuous monitoring mechanisms.
Ultimately, securing AI agent data is not merely a technical challenge but a strategic imperative. It requires a shift in security thinking, moving beyond traditional perimeter defenses to focus on data governance and access management within the context of intelligent automation. Proactive measures, such as the 90-day plan proposed by Herrell, are essential for navigating this evolving threat landscape.
The widespread integration of AI agents across industries necessitates a comprehensive security strategy that accounts for their unique capabilities and potential vulnerabilities. Failure to implement adequate controls could lead to significant data breaches, reputational damage, and regulatory penalties.