
KEV Adds Cisco, Chrome, Citrix, Fortinet Flaws; cPanel RCE Noted
CISA flags actively exploited Cisco, Chrome, Citrix, and Fortinet flaws; critical cPanel RCE also noted.
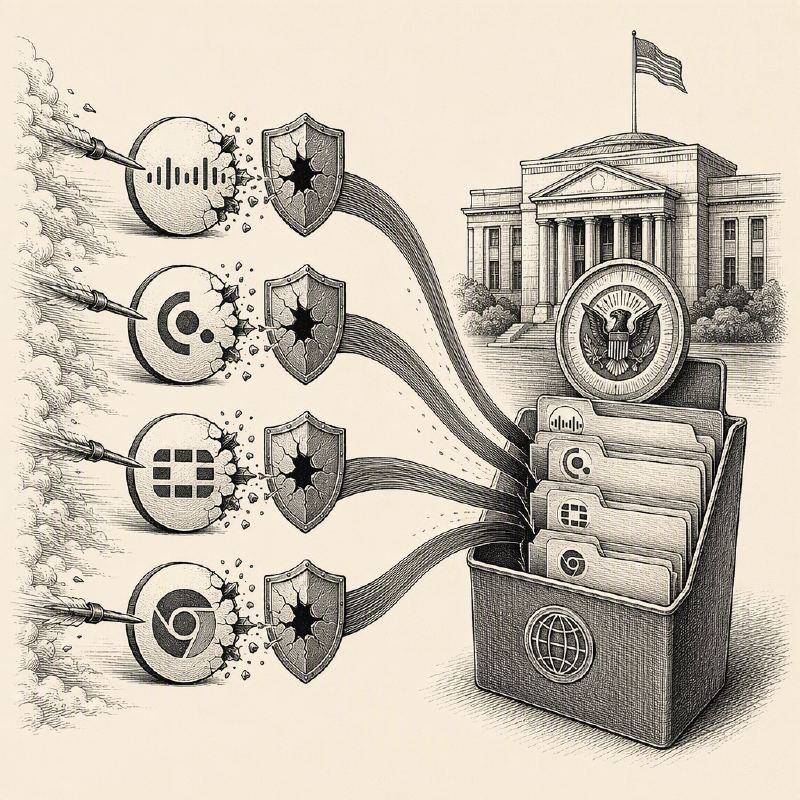
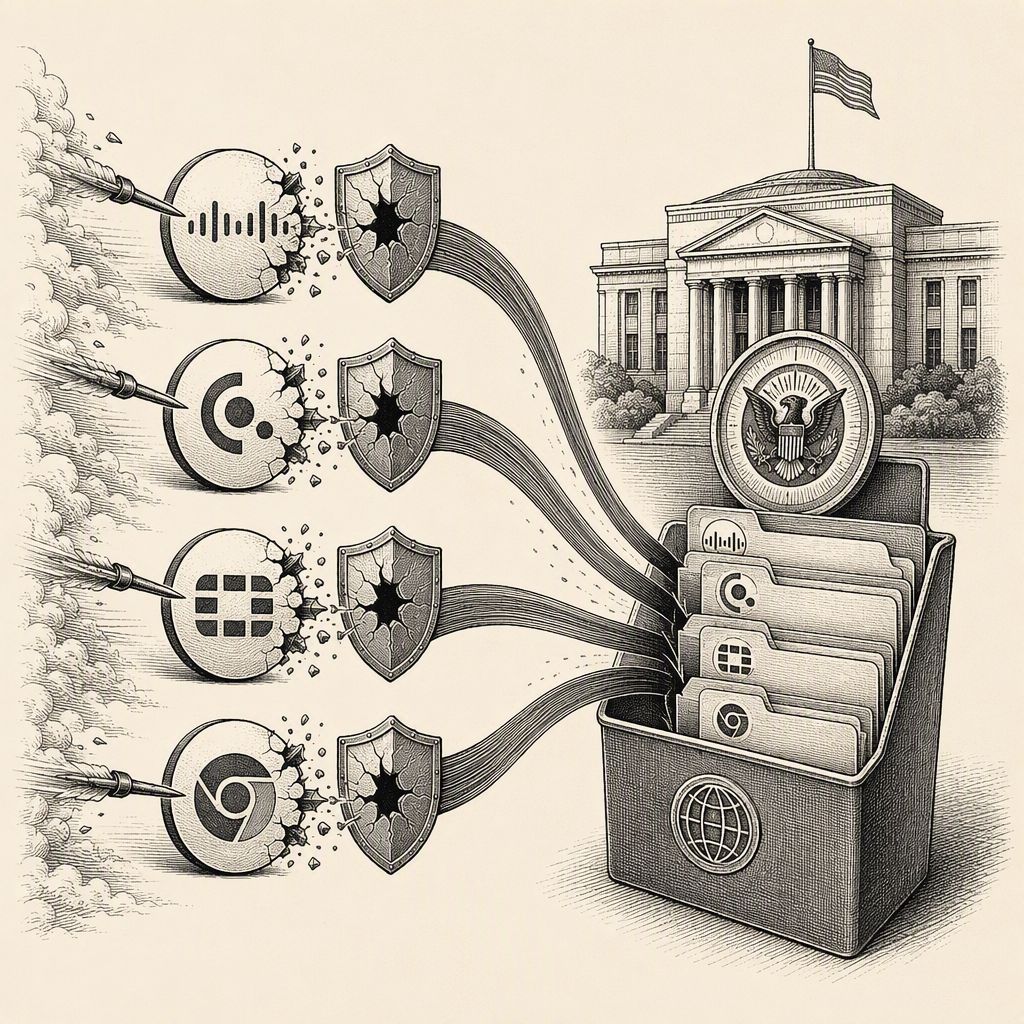
Cisco's Secure Firewall Management Center (FMC) is under active attack due to a critical authentication bypass vulnerability, CVE-2026-20079. This flaw allows unauthenticated, remote attackers to gain root access by executing script files on the device. The exploitation is severe enough that CISA has added it to its Known Exploited Vulnerabilities (KEV) catalog, with reports indicating its use by both nation-state actors and ransomware groups like Qilin. Cisco has released patches and urges immediate application. As The Hacker News reported, the vulnerability has been chained with other exploits, highlighting the urgency for remediation.
Google Chrome users are urged to update immediately to patch CVE-2026-87491, a critical out-of-bounds write vulnerability in the V8 JavaScript engine. This zero-day flaw, actively exploited in the wild, allows remote attackers to execute arbitrary code within the browser's sandbox via a crafted HTML page. Malwarebytes Labs noted, this is the seventh zero-day exploited in Chrome this year, underscoring the ongoing threats targeting web browsers. Chinese espionage groups have been observed chaining this vulnerability with others in Windows to compromise systems.
CISA has also flagged CVE-2026-19490, a critical vulnerability affecting Citrix NetScaler ADC and NetScaler Gateway, as actively exploited and added it to the KEV catalog. This authentication bypass flaw allows unauthenticated attackers to gain unauthorized access to sensitive systems. SecurityWeek reported that the vulnerability has been exploited in the wild, emphasizing the need for prompt patching. The scope of affected versions includes multiple release lines for both ADC and Gateway products.
Fortinet FortiOS and FortiSwitchManager are impacted by CVE-2025-25249, a heap-based buffer overflow vulnerability that is also being actively exploited and has been added to CISA's KEV catalog. This flaw can lead to code execution and has been observed in attacks deploying custom Node.js malware. Cyber Security News highlighted the critical nature of this vulnerability, affecting a wide range of versions across multiple product lines. Fortinet has released security advisories with patches for the affected versions.
A critical SQL injection vulnerability in cPanel's EmailTrack component, CVE-2026-67401, allows a mail-enabled account to achieve remote code execution as root. This means an attacker with a low-privileged hosting account could potentially gain full control of the server. The Hacker News detailed how this SQL injection flaw bypasses normal security controls, making it a significant risk for hosting providers and their customers. Users are advised to update cPanel to the latest version to mitigate this risk.