
SourceCodester: Five Vulnerabilities Including SQLi and XSS Disclosed Together
Five vulnerabilities, including four high-severity SQL injections and one XSS flaw, were disclosed together for SourceCodester products on September 23, 2026.
Key findings
- Five vulnerabilities disclosed on 2026-09-23 across two SourceCodester products.
- Four high-severity SQL injection flaws impact the Online Reviewer Management System 1.0.
- One medium-severity XSS vulnerability affects the Smart Attendance System with QR Code Scanner 1.0.
- Vulnerabilities allow remote exploitation via argument manipulation in PHP files.
- Urgent need for users to update systems and consult vendor advisories.
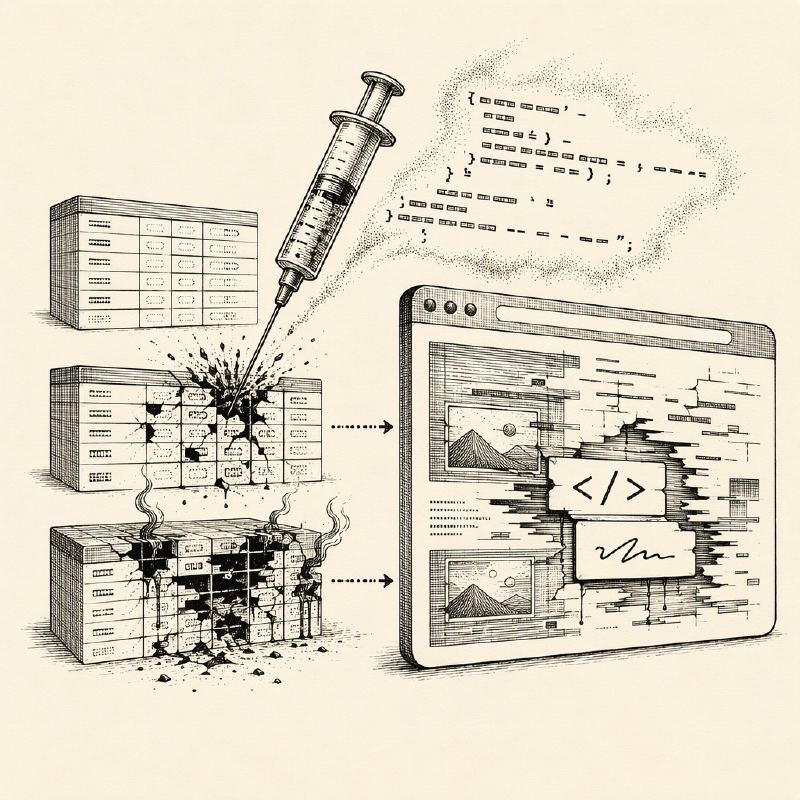
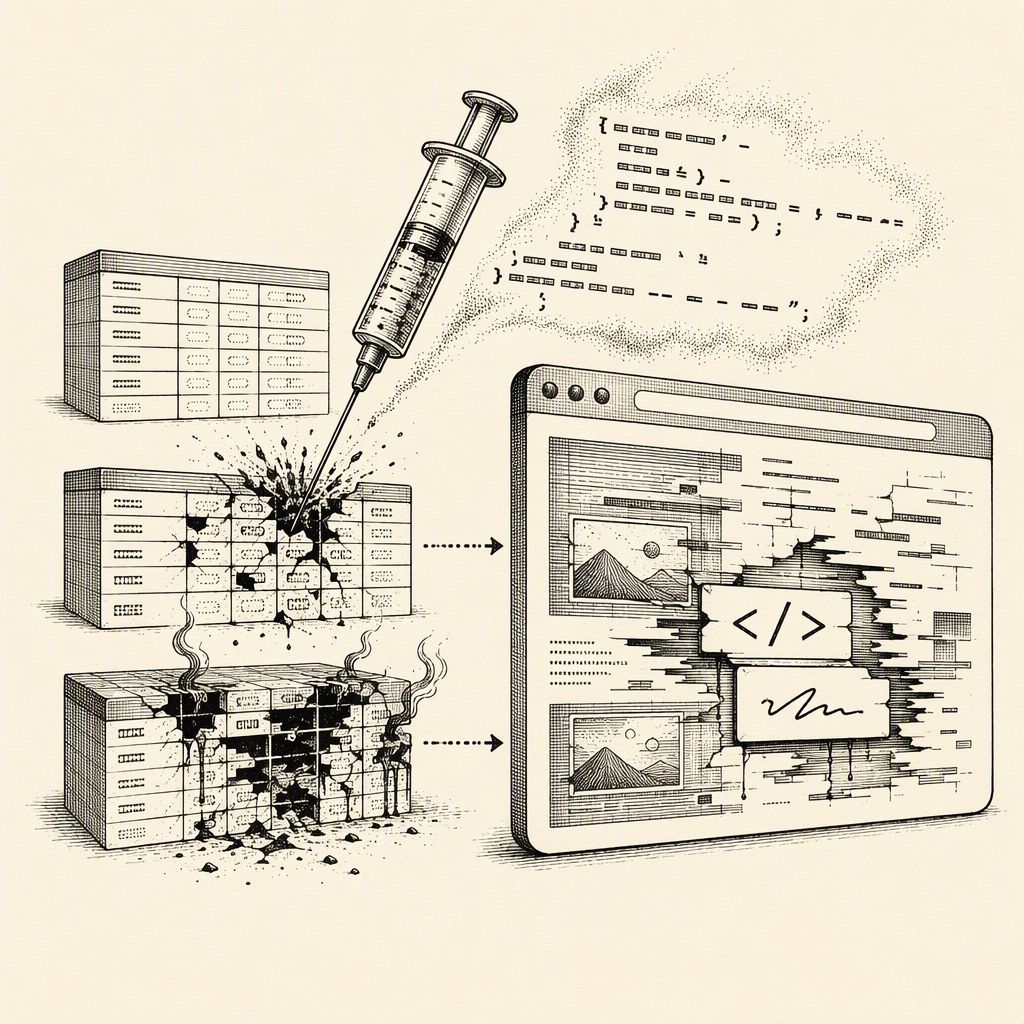
On September 23, 2026, a batch of five vulnerabilities was disclosed across two SourceCodester products, with four high-severity SQL injection flaws and one medium-severity cross-site scripting (XSS) vulnerability. The disclosures occurred within a two-hour window, indicating a coordinated disclosure event. These vulnerabilities pose a significant risk to users of the affected systems, potentially allowing remote attackers to compromise data and execute arbitrary code.
The SourceCodester Online Reviewer Management System 1.0 is particularly impacted, with four SQL injection vulnerabilities identified. CVE-2026-95927, CVE-2026-95926, CVE-2026-95925, and CVE-2026-95924 all stem from improper handling of arguments such as test_id and difficulty_id in various PHP files within the assessments directory. These flaws enable remote attackers to inject malicious SQL queries, potentially leading to unauthorized data access, modification, or deletion.
In addition to the SQL injection flaws, a cross-site scripting (XSS) vulnerability, CVE-2026-95957, was found in the SourceCodester Smart Attendance System with QR Code Scanner 1.0. This vulnerability resides in the student_signup.php file and is triggered by manipulating the full_name argument, allowing attackers to inject malicious scripts into the application, which can then be executed in the browsers of other users.
The disclosures highlight a critical need for users of these SourceCodester products to review and update their systems. While specific patch details or version information were not provided in the initial disclosures, the presence of multiple high-severity vulnerabilities underscores the urgency of addressing these security weaknesses. Users should consult SourceCodester's official advisories for the latest information on affected versions and available patches.
The coordinated disclosure of these vulnerabilities suggests a potential focus on these specific SourceCodester applications by threat actors. Users are advised to remain vigilant and apply any available security updates promptly to mitigate the risk of exploitation. Further investigation into the specific attack vectors and potential impact of these vulnerabilities is recommended for organizations utilizing these systems.