
MongoDB: 16 Vulnerabilities in Drivers, Libmongocrypt, and Ops Manager Disclosed Together
A batch of 16 MongoDB vulnerabilities, disclosed Oct 8-9, 2026, impact drivers, encryption, and Ops Manager, with risks ranging from DoS to memory corruption.
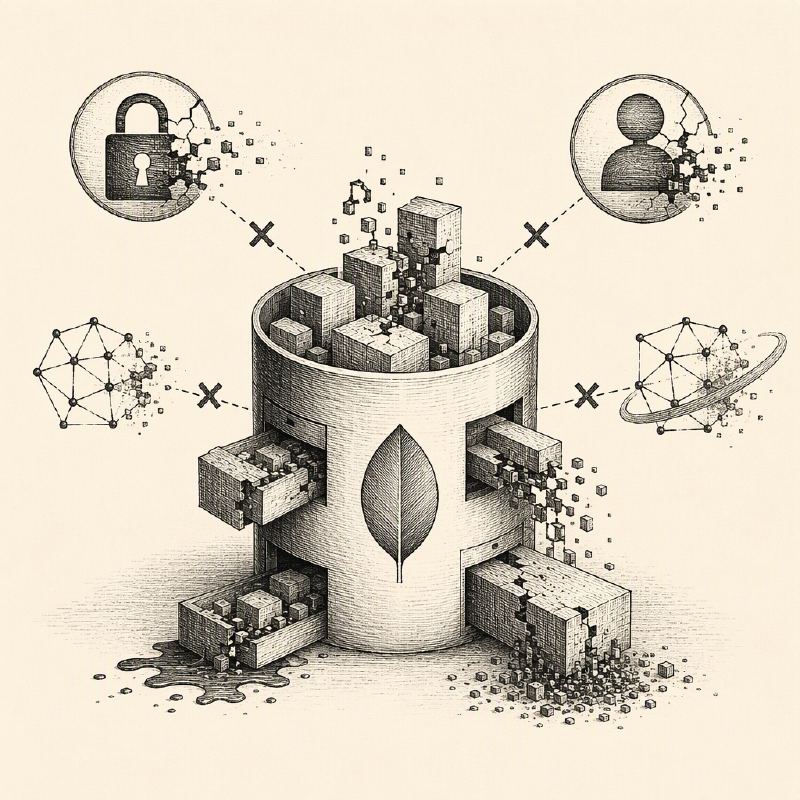
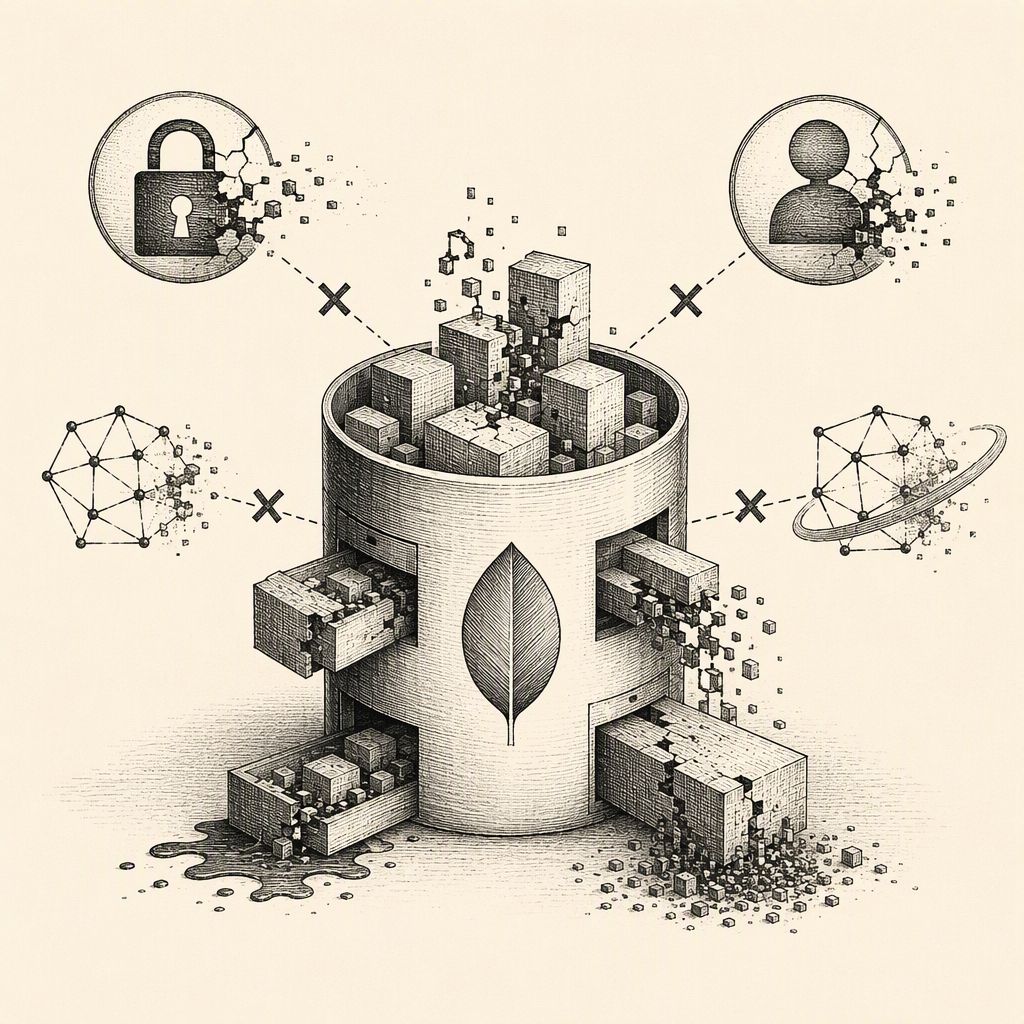
Key findings
- 16 MongoDB vulnerabilities disclosed between Oct 8-9, 2026, impacting drivers, libmongocrypt, and Ops Manager.
- Multiple BSON handling flaws across Python, PHP, Go, and C/C++ drivers can lead to crashes or data corruption.
- Encryption and authentication components are affected, with CVE-2026-106433 posing a high-severity risk due to key management issues.
- Ops Manager vulnerabilities include denial-of-service and unauthorized access to monitoring and authentication data.
- Users should consult MongoDB advisories for specific version information and apply patches promptly.
On October 8-9, 2026, a batch of 16 vulnerabilities was disclosed across various components of MongoDB, impacting its drivers and core libraries. These vulnerabilities, ranging in severity from Low to High, were disclosed over an 11-hour window, with the majority published on October 8th. The disclosures highlight issues within the BSON handling, encryption, and authentication mechanisms of MongoDB products.
Several vulnerabilities stem from improper handling of BSON data, a key format for MongoDB. CVE-2026-106435 in the Python Driver and CVE-2026-106436 and CVE-2026-106432 in the PHP Driver involve buffer overflows and invalid states due to malformed BSON, potentially leading to application termination. Similarly, the Go Driver is affected by CVE-2026-107325 and CVE-2026-107324, where improper BSON array length validation and integer overflows can result in runtime panics and denial-of-service conditions. The C Driver also faces BSON-related issues, including CVE-2026-106431, an off-by-one error in its bulk document writer, and CVE-2026-106430 in the C++ Driver, which mishandles NUL bytes in field names.
Encryption and authentication components are also implicated. CVE-2026-106434 in libmongocrypt can return unrecognized encrypted payloads unchanged, while CVE-2026-106433, also in libmongocrypt, suffers from improper state management during key document cleanup, potentially leading to memory corruption. A high-severity vulnerability, CVE-2026-106433, arises from duplicate masterKey fields in key documents. Another libmongocrypt vulnerability, CVE-2026-106429, involves an integer underflow in KMS endpoint parsing, leading to allocation failures and application termination.
Issues affecting Ops Manager include CVE-2026-87110, a denial-of-service vulnerability due to unauthenticated, un-rate-limited monitoring endpoint requests. CVE-2026-87109 allows an authenticated organization member to retrieve another member's pending authenticator enrollment seed, exposing sensitive authentication material. Additionally, CVE-2026-87108 permits an authenticated read-only user to retrieve monitoring records from different projects due to insufficient ownership validation.
The batch also includes CVE-2026-106438 in the C Driver, where incorrect Decimal128 string parsing can lead to values differing from the input text. CVE-2026-106428 in the C Driver's SCRAM authentication response parsing involves an out-of-bounds read due to malformed server-final messages.
These vulnerabilities underscore the importance of keeping MongoDB deployments and their associated drivers and libraries updated. Users are advised to consult MongoDB's official advisories for specific version information and patching guidance. The broad range of affected components indicates a need for comprehensive security reviews of MongoDB environments.
The timely disclosure of these vulnerabilities, clustered within a short period, allows security teams to address them collectively. Users should prioritize patching and review their configurations, especially for Ops Manager deployments and applications utilizing various MongoDB drivers.
The disclosed vulnerabilities affect multiple components of the MongoDB ecosystem, including its core database, drivers for various programming languages, and management tools like Ops Manager. The issues range from denial-of-service and information disclosure to memory corruption and application crashes.
The BSON parsing and handling vulnerabilities are particularly concerning, as BSON is fundamental to MongoDB's data storage and transfer. Flaws in these areas, such as buffer overflows and integer overflows, can be exploited by attackers to disrupt service or compromise system integrity.
The encryption and key management components also present significant risks. Vulnerabilities in libmongocrypt, especially those leading to memory corruption or application termination, highlight the need for robust security in cryptographic operations.
The Ops Manager vulnerabilities, while less severe in some cases, can still impact the manageability and availability of MongoDB deployments. Unauthorized access to monitoring data or denial-of-service attacks on management interfaces can have operational consequences.
MongoDB users should refer to the official security advisories for detailed information on affected versions and recommended remediation steps. Prompt application of patches and updates is crucial to mitigate the risks associated with this batch of vulnerabilities.
The coordinated disclosure of these 16 CVEs on October 8-9, 2026, provides a clear window for organizations to assess and address potential security gaps across their MongoDB infrastructure.
The vulnerabilities disclosed in this batch primarily relate to data handling, authentication, and encryption within MongoDB's ecosystem. The issues span across various components, including different language drivers (Python, PHP, Go, C, C++), core libraries like libmongocrypt, and the Ops Manager platform.
Several vulnerabilities are rooted in the improper parsing and handling of BSON (Binary JSON) data. For instance, CVE-2026-106435 (PHP Driver) and CVE-2026-106432 (PHP Driver) describe issues arising from incorrect size checks and integer overflows during BSON encoding, potentially leading to application termination or memory corruption. Similarly, CVE-2026-107325 and CVE-2026-107324 (Go Driver) detail problems with BSON array validation and integer overflows causing panics and denial-of-service conditions. The C Driver is also affected by BSON-related flaws, such as CVE-2026-106431 (off-by-one in bulk writer) and CVE-2026-106430 (C++ Driver, mishandling NUL bytes in names).
Encryption and authentication mechanisms are also targeted. CVE-2026-106434 (libmongocrypt) can lead to unrecognized encrypted payloads being processed, while CVE-2026-106433 (libmongocrypt) involves improper state management with duplicate masterKey fields, potentially causing memory corruption. CVE-2026-106429 (libmongocrypt) describes an integer underflow in KMS endpoint parsing that can terminate the application. Authentication responses are also affected, with CVE-2026-106428 (C Driver) detailing an out-of-bounds read in SCRAM response parsing.
Vulnerabilities impacting MongoDB Ops Manager include CVE-2026-87110, which allows unauthenticated denial-of-service through costly monitoring endpoint requests. CVE-2026-87109 permits authenticated users to access another member's pending authenticator enrollment seed, and CVE-2026-87108 exposes deployment metadata due to insufficient ownership validation in host monitoring records.
Other issues include CVE-2026-106438 (C Driver), concerning incorrect Decimal128 string parsing.
Users are strongly advised to consult MongoDB's official security advisories for detailed information on affected versions and the necessary steps to remediate these vulnerabilities. Prompt patching and updates are essential to secure MongoDB deployments against these newly disclosed threats. The coordinated nature of this disclosure allows for a comprehensive approach to security updates.