
Joomla Extensions: Four Critical RCE, SQLi, and Path Traversal Flaws Disclosed Together
Four critical vulnerabilities affecting Joomla extensions from lomart.fr and joomlaboat.com were disclosed on September 26, 2026, including RCE, path traversal, command injection, and SQLi.
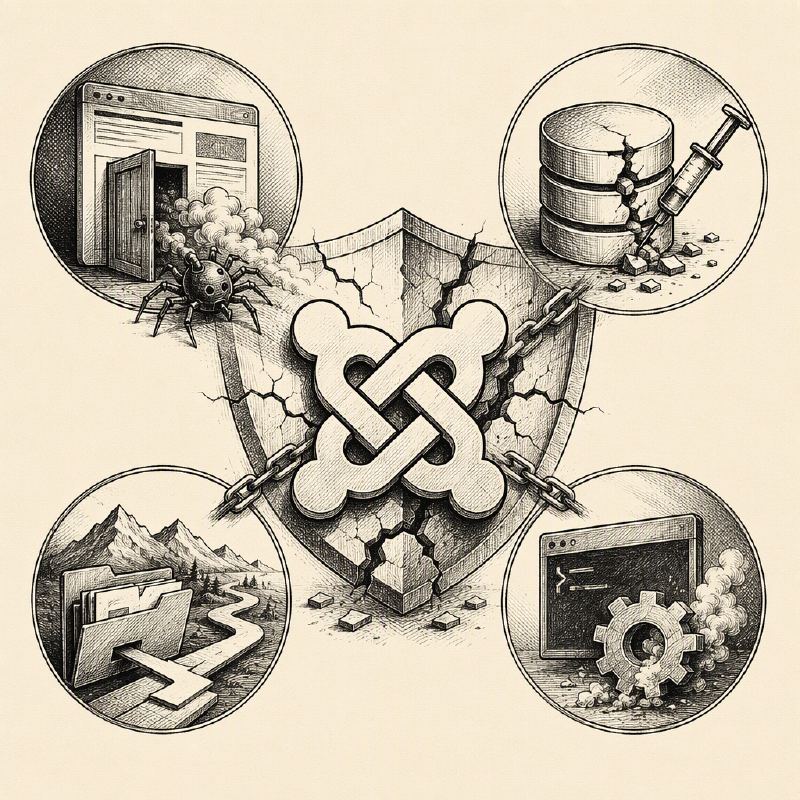
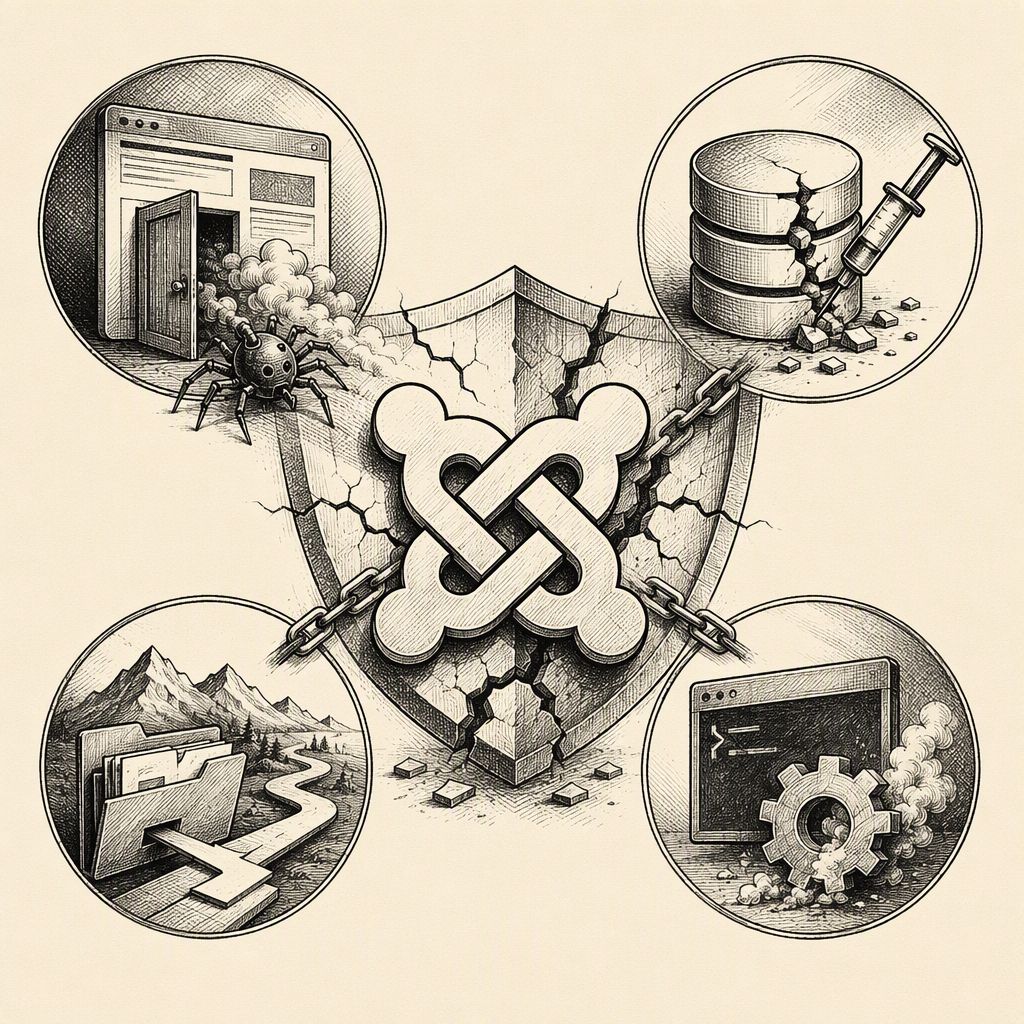
Key findings
- Four critical vulnerabilities disclosed on September 26, 2026, affect Joomla extensions from lomart.fr and joomlaboat.com.
- Flaws include unauthenticated remote code installation, path traversal, command injection, and SQL injection.
- The lomart.fr UP plugin (versions 5.0.0-5.2.0, 6.0.0-6.0.29) and joomlaboat.com YouTube Gallery (<5.7.3) are impacted.
- Immediate patching is recommended to prevent exploitation of these critical security issues.
On September 26, 2026, a batch of four critical vulnerabilities was disclosed, affecting Joomla extensions from two different vendors: lomart.fr and joomlaboat.com. The vulnerabilities, disclosed within a one-hour window, include remote code installation, path traversal, command injection, and SQL injection, posing significant risks to Joomla websites utilizing the affected plugins.
The vulnerabilities in the lomart.fr UP plugin extension, affecting versions 5.0.0 through 5.2.0 and 6.0.0 through 6.0.29, are particularly severe. CVE-2026-97163 allows for unauthenticated remote code installation, enabling attackers to execute arbitrary code on the server. Complementing this, CVE-2026-97161 involves various path traversal and file access vectors, which could be leveraged to access sensitive files or escalate privileges. Furthermore, CVE-2026-97160 enables authenticated users with elevated privileges to perform PHP command injection, offering another pathway for code execution.
The joomlaboat.com YouTube Gallery extension is impacted by CVE-2026-94130, a critical unauthenticated SQL injection vulnerability present in versions prior to 5.7.3. This flaw specifically targets the video search and sorting functionality, allowing attackers to inject malicious SQL commands into read queries, potentially leading to data breaches or manipulation.
The coordinated disclosure of these critical vulnerabilities highlights a significant risk for Joomla administrators. The severity of the flaws, ranging from remote code execution to SQL injection, necessitates immediate attention to patching and security updates. Users of the lomart.fr UP plugin and the joomlaboat.com YouTube Gallery extension should prioritize updating to secure versions to mitigate these threats.
As of the disclosure, there is no immediate information regarding active exploitation in the wild for this specific batch. However, the critical nature of these vulnerabilities means that unpatched sites are highly attractive targets for automated attacks and malicious actors. Administrators are strongly advised to apply patches as soon as possible. The affected versions for the UP plugin are 5.0.0-5.2.0 and 6.0.0-6.0.29, and for the YouTube Gallery extension, it is versions prior to 5.7.3. Patches should be applied to address these security concerns.
This batch of vulnerabilities underscores the importance of regularly auditing and updating third-party extensions within a Joomla environment. The simultaneous disclosure of multiple critical flaws from different vendors emphasizes the need for a proactive security posture, including timely application of security patches and vigilant monitoring for any suspicious activity. Staying informed about security advisories and promptly addressing disclosed vulnerabilities is crucial for maintaining the integrity and security of Joomla websites.