
Cisagov: Six Auth Bypass and Privilege Escalation Flaws Disclosed Together
Six Cisagov product vulnerabilities, including three critical flaws, were disclosed on 2026-09-15, primarily related to authentication and authorization weaknesses.
Key findings
- Six Cisagov product vulnerabilities disclosed together on 2026-09-15, including three critical flaws.
- Vulnerabilities primarily exploit authentication and authorization weaknesses, allowing privileged access and control.
- Affected products include mySCADA myPRO Manager and Digital Watchdog VMAX DVR/NVR series.
- Exploitation could lead to full administrative control, data disclosure, and network pivoting.
- CISA advisories highlight potential for SMS message interception and plaintext credential exposure.
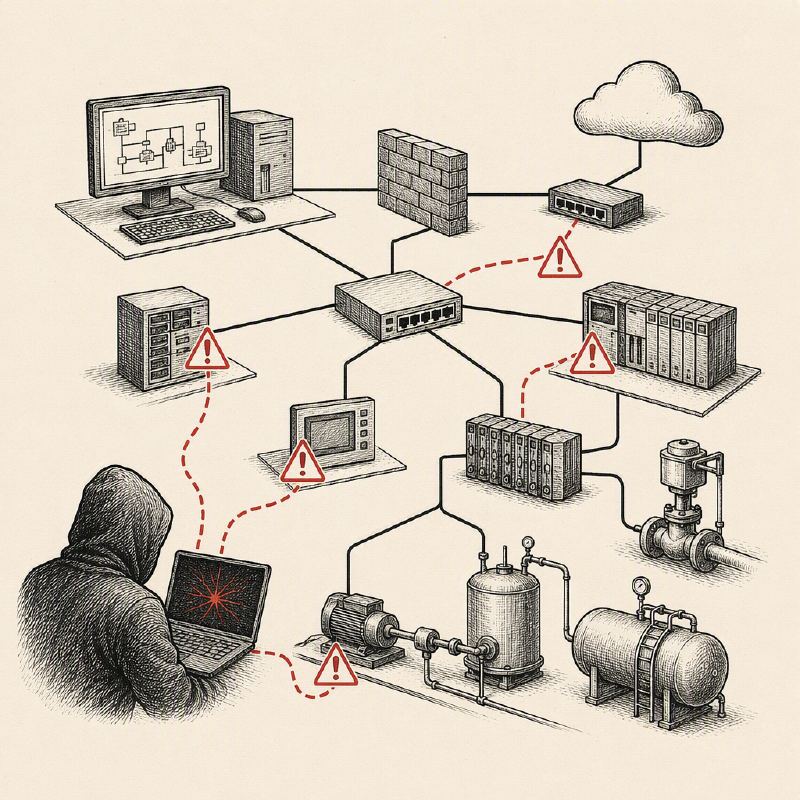
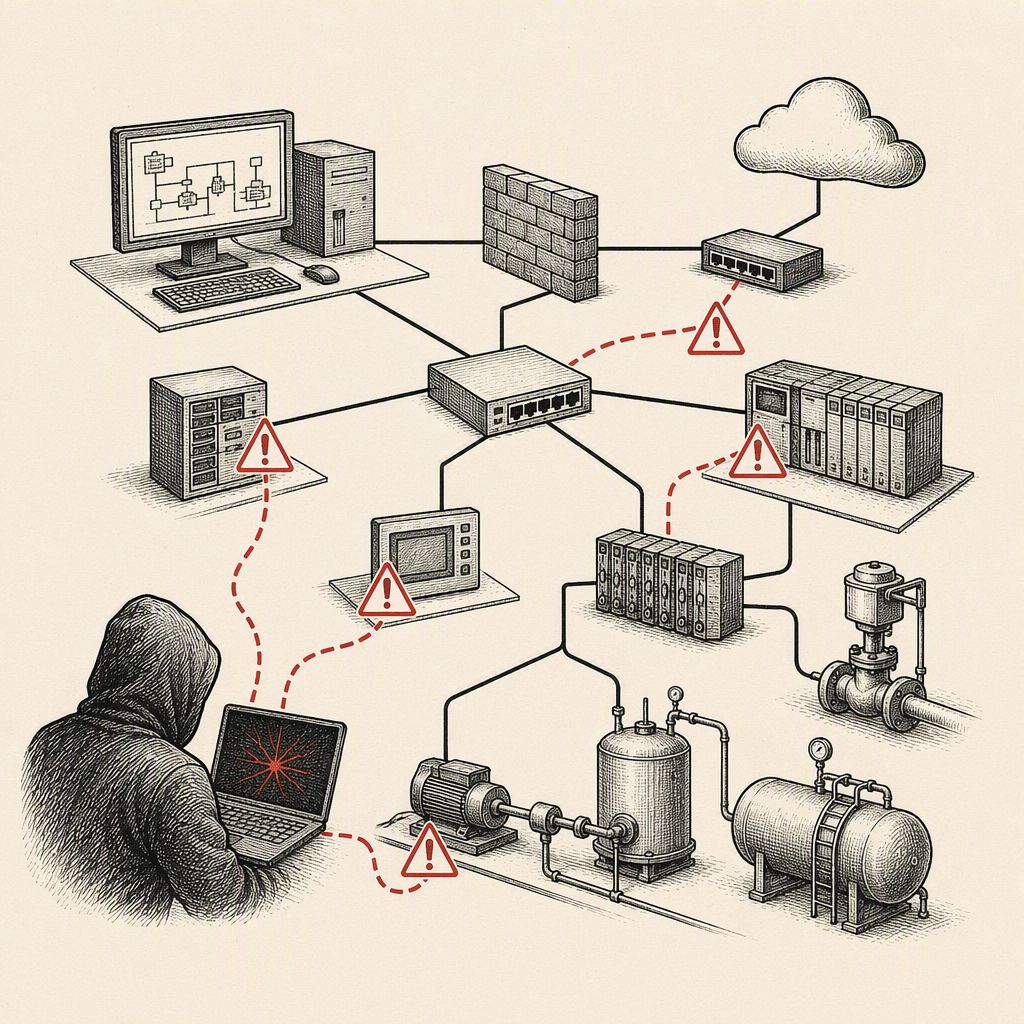
On September 15, 2026, a batch of six vulnerabilities was disclosed affecting Cisagov products, with three critical, two high, and one medium severity flaw. These vulnerabilities, disclosed within a one-hour window, primarily revolve around authentication and authorization weaknesses, potentially allowing attackers to gain privileged access and control over affected devices. The disclosures were detailed in CISA ICS Advisories, highlighting the potential impact on critical infrastructure sectors.
Several vulnerabilities stem from missing or improperly enforced authentication. CVE-2026-73807, a critical CVSS 9.8 vulnerability in mySCADA myPRO Manager, allows unauthenticated attackers to access privileged management functions via the command API. Similarly, CVE-2026-68070, a high severity flaw (CVSS 8.8), involves missing authentication for a critical function, enabling an attacker to execute commands as root. CVE-2026-66887, another critical vulnerability (CVSS 9.6), involves missing authorization on state-changing CGIs and a lack of session checks.
Other critical vulnerabilities include CVE-2026-66890 (CVSS 9.6), which involves hard-coded credentials allowing root-level file access via FTP. CVE-2026-68953, a medium severity flaw (CVSS 6.5), permits unauthenticated remote attackers to bypass authentication and disclose sensitive device information, including administrator credentials in plaintext, through crafted HTTP(S) requests. Lastly, CVE-2026-66372, a medium severity vulnerability (CVSS 6.8), stems from the use of insufficiently random values for web session tokens, making them predictable.
The CISA advisories indicate that exploitation of these vulnerabilities could lead to attackers gaining full administrative control of devices. This control could allow them to view live and recorded surveillance feeds, alter device configurations, and use the compromised device as a pivot point into a network. For CVE-2026-73807, CISA specifically notes the potential for attackers to send arbitrary SMS messages through a connected GSM modem.
Affected products include mySCADA myPRO Manager versions up to and including 2.1 for CVE-2026-73807. Digital Watchdog VMAX DVR and NVR Product Lineups, including VMAX A1 G4 DVRs, VMAX IP G4 NVRs, VMAX A1 PLUS, and VA1G4 Recorders, are affected by the other disclosed CVEs. The advisories state that for these Digital Watchdog products, all versions are affected. Patches and specific mitigation details were not immediately available in the provided advisories, emphasizing the need for users to consult vendor releases.
This batch of vulnerabilities underscores the importance of robust authentication and authorization mechanisms in industrial control systems and surveillance equipment. Users of Cisagov products, particularly mySCADA myPRO Manager and Digital Watchdog VMAX series, should prioritize reviewing CISA advisories and applying any available patches or workarounds as soon as possible to mitigate the risk of unauthorized access and control. The coordinated disclosure suggests a focused effort to address a significant security posture issue within these product lines.