
Adobe Campaign Classic: 17 Critical Vulnerabilities Disclosed Together, Including Code Injection and SSRF
Adobe Campaign Classic faces a critical security crisis with 17 vulnerabilities disclosed on September 22, 2026, including multiple flaws with CVSSv3 scores of 10.0.
Key findings
- 17 critical vulnerabilities disclosed simultaneously in Adobe Campaign Classic on September 22, 2026.
- Multiple code injection flaws with CVSSv3 scores up to 10.0 could lead to arbitrary code execution.
- Server-Side Request Forgery (SSRF) vulnerabilities allow for privilege escalation and internal resource access.
- SQL injection and improper input validation flaws also present significant risks.
- All affected versions require immediate patching as per Adobe's security advisories.
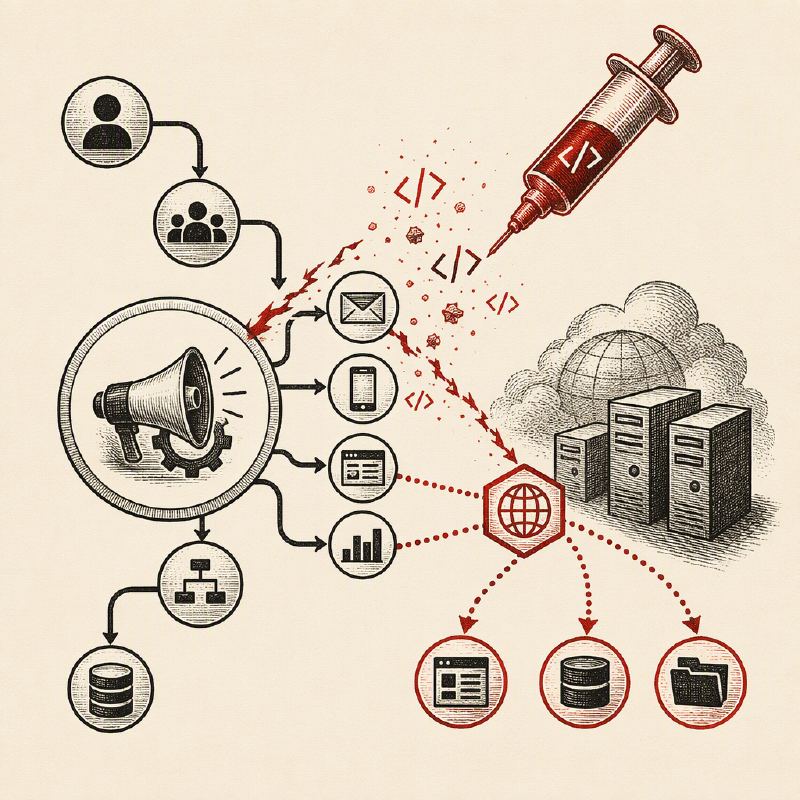
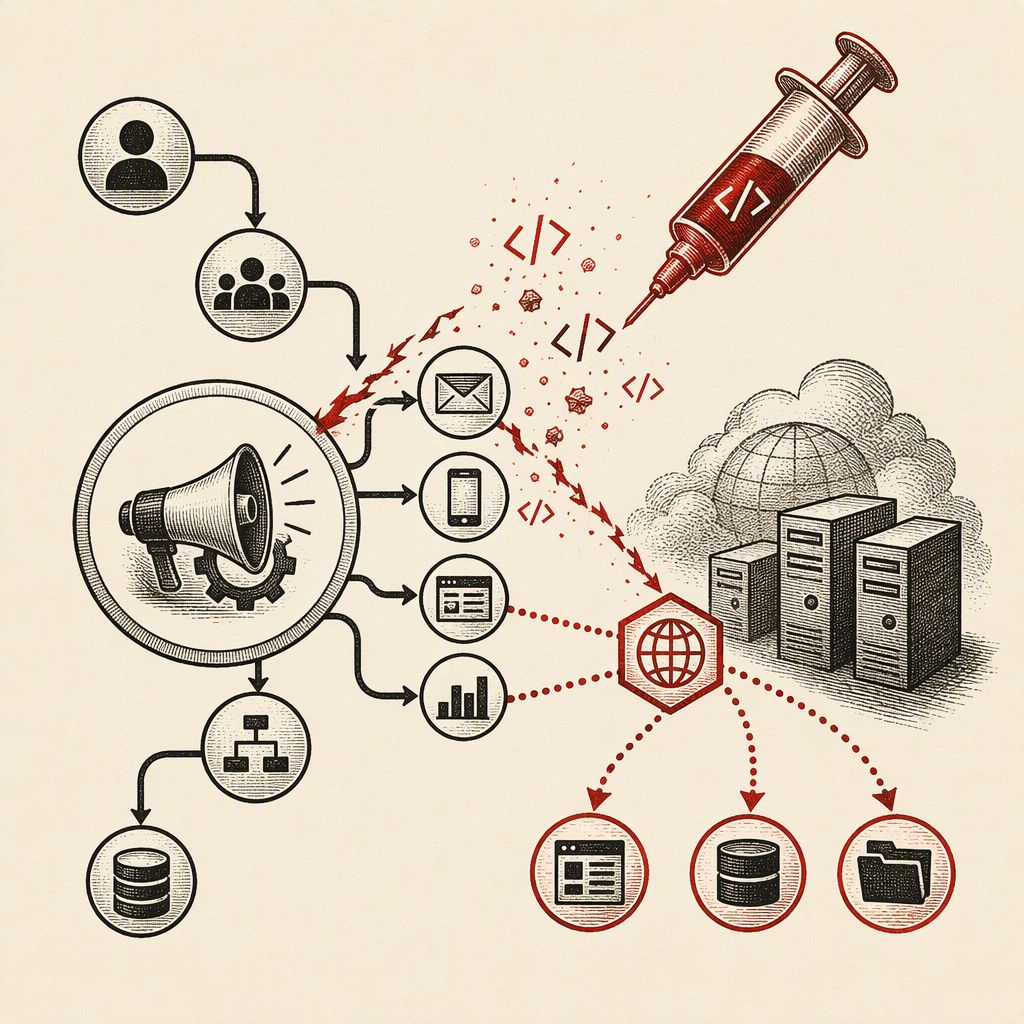
On September 22, 2026, Adobe disclosed a significant batch of 17 vulnerabilities affecting Adobe Campaign Classic (ACC). The vulnerabilities, all published on the same day, span critical severity ratings, with several reaching the maximum CVSSv3 score of 10.0. These flaws primarily revolve around code injection, server-side request forgery (SSRF), SQL injection, and improper input validation, collectively posing a severe risk to users of the marketing automation software.
The batch includes multiple instances of 'Code Injection' vulnerabilities (CVE-2026-89276, CVE-2026-89275, CVE-2026-84412, CVE-2026-75721, CVE-2026-75703, CVE-2026-75699, CVE-2026-73369), all rated as Critical with CVSSv3 scores of 9.9 or 10.0. These flaws could allow attackers to execute arbitrary code in the context of the current user, with some requiring no user interaction for exploitation.
Server-Side Request Forgery (SSRF) vulnerabilities are also prominent, with CVE-2026-83660, CVE-2026-82443, and CVE-2026-82013 identified. These Critical severity flaws (CVSSv3 9.6-9.9) could lead to privilege escalation and allow attackers to access internal resources.
SQL Injection vulnerabilities are represented by CVE-2026-82011, CVE-2026-82010, and CVE-2026-82009. These range in severity from Critical (CVSSv3 9.1-9.9) and could result in security feature bypass or arbitrary code execution.
Further compounding the risk are Improper Input Validation vulnerabilities, including CVE-2026-82008 (Critical, CVSSv3 9.9) and CVE-2026-82003 (High, CVSSv3 8.5), both of which could lead to arbitrary code execution. Additionally, Incorrect Authorization vulnerabilities, CVE-2026-75728 and CVE-2026-75723, rated Critical with CVSSv3 scores up to 10.0, could also enable arbitrary code execution.
The widespread nature and high severity of these vulnerabilities underscore the critical need for Adobe Campaign Classic users to apply available patches immediately. The lack of specific threat actor or exploitation details in the advisories means that organizations must proactively secure their deployments against potential attacks targeting these weaknesses.
Adobe has released patches to address these vulnerabilities. Users are strongly advised to consult Adobe's security bulletins for specific version information and apply the necessary updates to mitigate the risks associated with these critical flaws.
This coordinated disclosure of numerous high-severity vulnerabilities highlights a significant security posture concern for Adobe Campaign Classic. Organizations relying on this platform should prioritize patching and review their security configurations to prevent potential exploitation.
Key findings include the sheer volume of critical vulnerabilities disclosed simultaneously, the prevalence of code injection and SSRF flaws, and the potential for arbitrary code execution and privilege escalation.
The vulnerabilities disclosed include: CVE-2026-89276, CVE-2026-89275, CVE-2026-84412, CVE-2026-83660, CVE-2026-82443, CVE-2026-82013, CVE-2026-82011, CVE-2026-82010, CVE-2026-82009, CVE-2026-82008, CVE-2026-82003, CVE-2026-75728, CVE-2026-75723, CVE-2026-75721, CVE-2026-75703, CVE-2026-75699, CVE-2026-73369.